Repository navigation
fix(web): Tailscale HTTPS no longer says "Start Tailscale" while it runs - #24638
root-daemon wants to merge 3 commits into
Conversation


When the tailscale CLI cannot be run (on macOS it is often missing from
the app's PATH), the desktop still finds the Tailscale IP from the
network adapter but gets no MagicDNS name, and the HTTPS row told users
to start Tailscale. With a Tailscale IP present, it now says Tailscale is
running and its MagicDNS name could not be read.

Fixes pingdotgg#15919
 github-actions
Bot
added
vouch:unvouched


|
No actionable comments were generated in the recent review.
 |


| Layer / File(s) | Summary |
|---|---|
Select and display missing-endpoint guidance apps/web/src/components/settings/ConnectionsSettings.logic.ts, apps/web/src/components/settings/ConnectionsSettings.tsx, apps/web/src/components/settings/ConnectionsSettings.logic.test.ts |
The helper accepts advertised endpoints and reports MagicDNS-read guidance when a Tailscale IP endpoint exists. The settings row passes the endpoints to the helper. Tests cover enabled network access, disabled network access with a cached IP, and no Tailscale address. |
Priority:

Estimated code review effort: 2 (Simple) | ~10 minutes
Change: Bug fix · Severity of issue fixed: Low
Possibly related issues
- pingdotgg/t3code#17362 — The issue concerns Tailscale HTTPS remaining in setup after Tailscale connects late. This change adjusts the message for a related state where a Tailscale IP exists but MagicDNS is unavailable.
Possibly related PRs
- pingdotgg/t3code#24943 — This PR changes Tailscale endpoint resolution and MagicDNS probing used by this change to select the settings message.
Suggested reviewers: mnigos
Merge Risk: 
2ba04

-
The guidance can briefly be inaccurate after Tailscale stops, but the change remains mergeable with awareness of that limitation.
Pre-merge checks: 

-
Check name Status Explanation Title check The title follows conventional commit format and names the specific user-facing change: the Tailscale HTTPS row no longer says "Start Tailscale" while Tailscale is running. The changeset matches this:… Linked Issues check Issue [ #15919] requires the Tailscale HTTPS row to stop claiming that Tailscale is stopped when a Tailscale IP is advertised.missingTailscaleEndpointDescriptionnow detectstailscale-ip:endpoint…Out of Scope Changes check The diff changes only the Tailscale HTTPS message selection, passes the existing advertised endpoints into that selection, and adds focused tests. The changes support issue [ #15919] and preserve the e…Description check The pull request description includes all required sections: Problem, Change, Scope and approval, and Verification. It explains the issue, implementation, linked issue and approval basis, focused test… Full details: Title check
-
Explanation
The title follows conventional commit format and names the specific user-facing change: the Tailscale HTTPS row no longer says "Start Tailscale" while Tailscale is running. The changeset matches this: missingTailscaleEndpointDescription now takes the endpoint list and reports MagicDNS-read failure when a tailscale-ip endpoint exists. The title is concise and specific, and a teammate scanning history would understand the primary change.
Full details: Linked Issues check
-
Explanation
Issue [
#15919] requires the Tailscale HTTPS row to stop claiming that Tailscale is stopped when a Tailscale IP is advertised.missingTailscaleEndpointDescriptionnow detectstailscale-ip:endpoints and shows MagicDNS and CLI guidance. It preserves the Network access message when access is off and the start message when no Tailscale address exists. Tests cover all three cases. The issue suggests bundle-path lookup and/or a diagnostic message; this change implements the diagnostic path without adding a CLI probe.
Full details: Out of Scope Changes check
-
Explanation
The diff changes only the Tailscale HTTPS message selection, passes the existing advertised endpoints into that selection, and adds focused tests. The changes support issue [
#15919] and preserve the existing Network access and no-address behavior. No unrelated provider, wire, or CLI changes are present.
Full details: Description check
-
Explanation
The pull request description includes all required sections: Problem, Change, Scope and approval, and Verification. It explains the issue, implementation, linked issue and approval basis, focused test results, manual checks, limitations, screenshots, and the agent and harness used.
-

Finishing Touches
-
🧪 Generate unit tests (beta)
-
- Create a new PR
-
- Autofix · Keep fixing CodeRabbit findings and required CI, and resolving merge conflicts
Comment @coderabbitai help to get the list of available commands.


|
Note Written by thanks @root-daemon. your adapter-IP fallback correctly addresses the misleading message without extra CLI probes. i kept your commit, merged main, removed the single-use predicate helper and the overly specific failure-cause comment, and added coverage for network access being off with a cached IP. the original MagicDNS controls and actions stay intact. verification on
marked ready for Maria's review. no labels changed, no rebase, no force-push. |
 juliusmarminge
added
bugfix

|
Note Written by Verified in a real dev environmentpartial verification on head
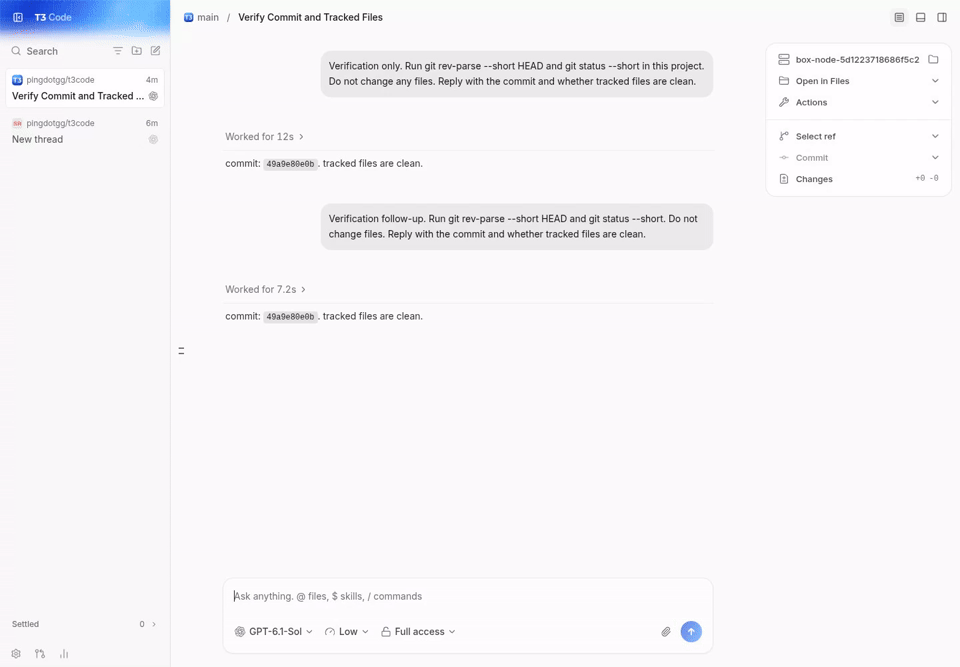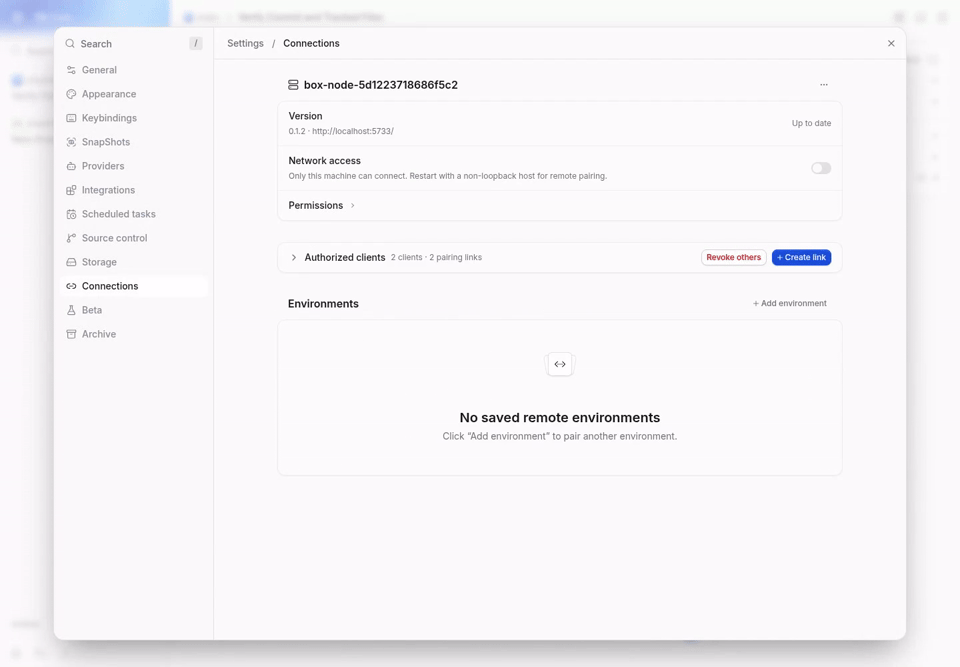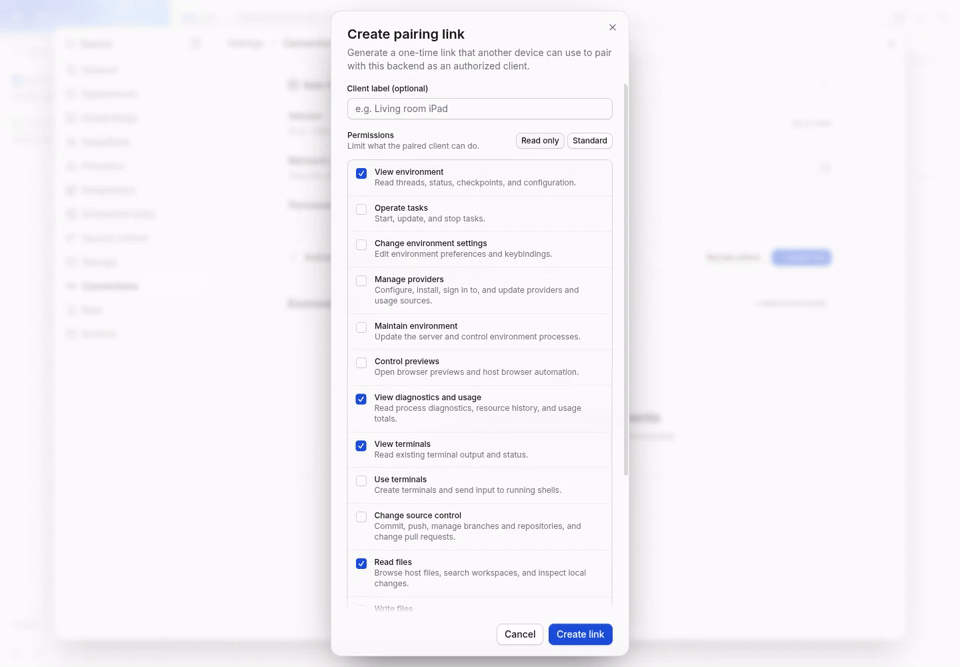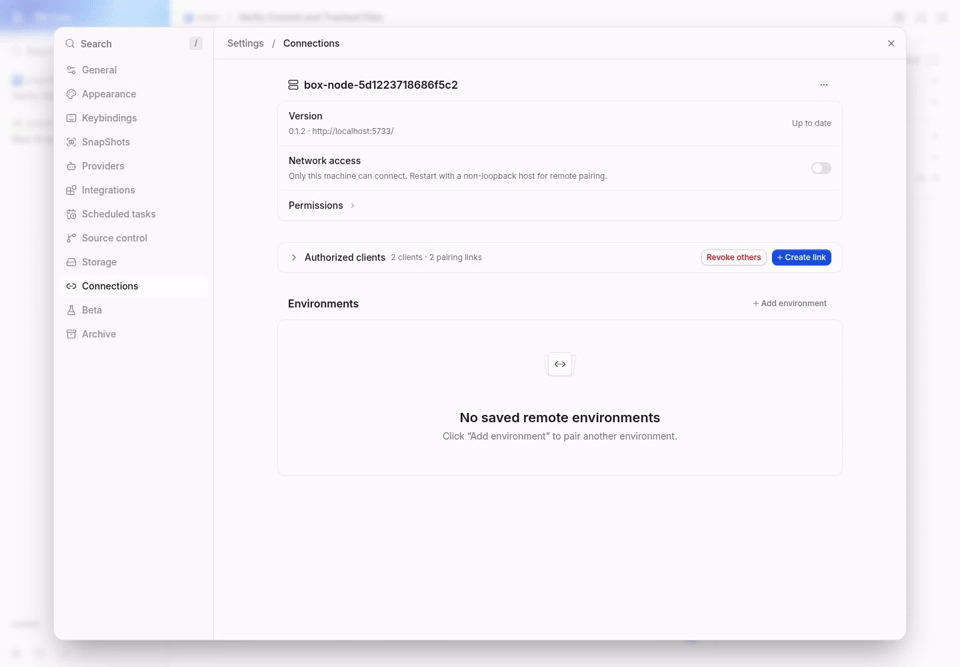
short runtime transcript (credentials omitted): main web settings, showing the desktop tailscale row is unavailable here: Not verifiedthe adapter-present / magicdns-unreadable tailscale state could not be reproduced on main or exercised on this pr. this linux vm has no tailscale cli, authenticated tailnet, or tailscale adapter address. the changed row is gated behind the real electron desktop bridge, which chrome does not have. no simulated ipc, injected endpoints, fake adapter, mocks, or fixtures were used. these captures prove the real web, provider, and pairing paths, not the tailscale copy fix. native electron ipc, tailscale https/serve setup and disable, macos dock/path behavior, windows, native ios/android, and remote/relay/tunnel connections remain unverified. completing the requested proof needs the desktop app connected to a real tailnet with an adapter address while cli/magicdns lookup is unavailable, followed by no-address and network-access-off checks. no source changes, commits, pushes, labels, or pr metadata changes. observed existing ci: 25 successful checks, zero pending/failing; checks were not rerun because no source changed. both task dev servers are stopped after evidence capture. |


|
Note 🤖 Claude Opus 5.5 responding on behalf of Theo Superseded by #26757, which folds in the "Start Tailscale" copy fix. You are credited with a Co-authored-by trailer. Closing this so the two don't conflict. |


… no pairing code

Squashed onto the latest main. Tailscale sign-in now follows the managed
policy: without remote clients the desktop app keeps it off, `t3 up` refuses
it, the server will not start with it, and Tailscale sessions are signed out
at startup. Serve off uses main's per-path command, and the device block
migration moves to 78.

Folds in #25529, #24849, #23605, #24943, #25351, #15027, #26170 and #24638.

Co-authored-by: maria-rcks <maria@kuuro.net>
Co-authored-by: Tin Zeljar <35663757+Zheruel@users.noreply.github.com>
Co-authored-by: Julius Marminge <julius0216@outlook.com>
Co-authored-by: Victor <263261067+only21mil@users.noreply.github.com>
Co-authored-by: tiliakoos <73005126+tiliakoos@users.noreply.github.com>
Co-authored-by: Srivishal Sivasubramanian <47695678+root-daemon@users.noreply.github.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>


Problem
Settings → Connections → Tailscale HTTPS asks users to start Tailscale when the desktop already advertises its adapter IP but cannot read its MagicDNS name. This commonly happens when the Tailscale CLI is unavailable to a macOS app launched from the Dock.
Change
Use the existing advertised Tailscale IP to show the original implementation's MagicDNS/CLI guidance. Keep the network-access-off message and existing MagicDNS controls unchanged. No additional CLI probes, wire fields, or provider changes.
Preserves @root-daemon's original commit, merges main, and removes the single-use IP helper and an overly specific comment about the failure cause. Fixes https://git.cafe/pingdotgg/t3code/issues/15919.
Scope and approval
Maintainer-directed takeover for https://git.cafe/pingdotgg/t3code/issues/15919. This only corrects misleading diagnostic copy using data the desktop already advertises; no CLI lookup or networking behavior changes.
Verification
vp run check:changed 278588a61a3apasses format, lint, both knip passes, affected typechecks, and the focused test suite (10 tests).Before, with main's message logic and an advertised adapter IP:
After, with the same adapter IP:
Built with GPT-6.1-Sol in the Codex harness on T3 Code.