Repository navigation
Sync with Microsoft ONNX Runtime - 30102026 - #1375
Merged
Merged
Conversation


microsoft#33583) ### Description Guard `Sve2p1HalfGemmKernelName` with the union of its two consumer conditions: the KleidiAI test hook and kernel logging. Builds without either consumer no longer declare the unused constant; the string and both consumers are unchanged. ### Motivation and Context Building `36f07f760dccb74a96d0a3c851163d6448bdfd21` with Clang, `USE_KLEIDIAI`, `MLAS_ENABLE_TEST_HOOKS` undefined (for example, `onnxruntime_BUILD_UNIT_TESTS=OFF`), and `KLEIDIAI_KERNEL_LOGGING=0` fails because `-Wall` enables the unused-constant warning and the build uses `-Werror`: ```text halfgemm_kleidiai.cpp:26:23: error: unused variable 'Sve2p1HalfGemmKernelName' [-Werror,-Wunused-const-variable] ``` The name is used by `GetKleidiAIHalfGemmKernelNameForTesting` when test hooks and KleidiAI are enabled, and by `KLEIDIAI_KERNEL_LOG` when kernel logging is enabled. Debug logging alone does not consume it. The guard keeps the declaration out of configurations that never use it. `[[maybe_unused]]` on the declaration would also work; happy to switch if preferred. Validation ran on 2026-10-24 against `36f07f760dccb74a96d0a3c851163d6448bdfd21`; the affected file and its build closure are unchanged at `bd6010c0e1ff09b016c3fa6c9c818b6699ccd9b9` (checked 2026-10-25). Validation used offline Docker on Linux arm64, Clang 17 (Swift LLVM fork) with GCC 12 libstdc++, and the actual generated whole-translation-unit command (`-O3 -std=gnu++20 -Wall -Wextra -Werror`). The six diagnostic combinations below were compiled before and after the fix; only diagnostic macros and output paths were varied. | Diagnostic combination | Unmodified main | This change | | --- | --- | --- | | No test hooks; kernel logging off | Expected unused-name error | Pass | | Test hooks defined; kernel logging off | Pass | Pass | | No test hooks; kernel logging on | Pass | Pass | | Test hooks defined; kernel logging on | Pass | Pass | | Debug logging only | Expected unused-name error | Pass | | Test hooks defined; debug logging on; kernel logging off | Pass | Pass | All 12 expected outcomes were verified. The complete `onnxruntime_mlas` static-library target then built successfully (457 build steps). Existing source hashes were checked before and after validation. Upstream's configured format linter explicitly excludes MLAS, and no configured linter matched this file. The C++ unit suite, full ORT wheel, SVE2.1 hardware execution, other compilers/platforms and hosted CI were not run. This change addresses the compiler error only. 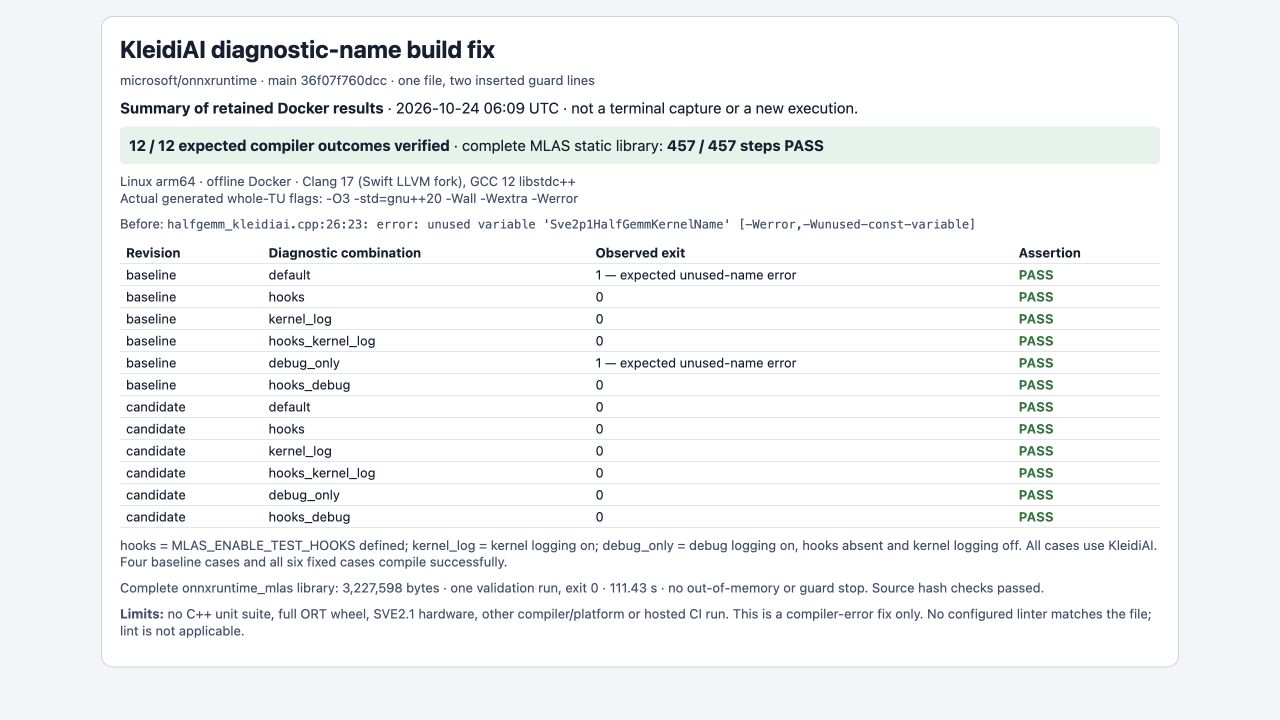


### Description

the CPU `TopK` comparators use `>` / `<` and `==` on the values , so
with a NaN in the input they are not a strict weak ordering : a NaN is
neither greater , smaller nor equal to anything . the result depends on
where the NaN sits and which path runs , and `std::nth_element` /
`std::sort` are handed a comparator they do not support .

| input | k | largest | before | after |
| --- | --- | --- | --- | --- |
| `[1, NaN, 3, 2]` | 2 | 1 | `[1, NaN]` | `[NaN, 3]` |
| `[1, NaN, 3, 2, NaN, -1, 5, 0]` | 1 | 1 | `5` at 6 | `NaN` at 1 |

NaN now ranks above every other value and equal values , NaN included ,
keep the lower index first . that is what the CUDA kernel already does ,
`HybridNaNUsesStablePackedOrdering` checks it , so CPU and CUDA agree .
integer types compile to the same comparisons as before .

the `k == 1` scan keeps its plain comparison , which the compiler
vectorizes , and folds a NaN check into the same loop . only a row that
holds a NaN is scanned again with the NaN aware comparison . a
standalone copy of the loops on 4M floats without NaN , clang -O2 on
arm64 :

| path | before | after |
| --- | --- | --- |
| `k == 1` scan | 1.97 ms | 1.96 ms |
| full index sort | 324 ms | 323 ms |

putting the NaN check straight into the `k == 1` comparison instead made
that loop about 6x slower , which is why it has the second pass .

`TopKOperator.NaNIsLargest` covers the scan ( k = 1 ) , the heap ( k = 3
) and `nth_element` ( k = 6 and 8 ) for largest and smallest , float and
double , opset 11 and 24 , on the CPU EP . it fails before the change .
`onnxruntime_provider_test
--gtest_filter='*TopK*:*BeamSearch*:*GreedySearch*:*Sampling*'` , 100
tests , passes on macOS arm64 , and `lintrunner` is clean .

### Motivation and Context

found by running single node models through the ONNX reference evaluator
and onnxruntime 1.31 side by side . TopK of `[1, NaN, 3, 2]` with k = 2
gave `[1, NaN]` here , 1 being the smallest value in the input . the
spec does not define a NaN order , so this follows the CUDA EP . no
existing issue that I could find .

Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>

### Description

Avoid division by zero in MatMulComputeHelper when a batch-transposed
input has a zero leading dimension. Empty operands now have zero matrix
offsets, allowing the existing empty-output and zero-K handling to run
while keeping transpose fusion enabled.

Fixes microsoft#33244.

### Validation

Windows x64, Release CPU build, based on c55286e:

- Before the fix, the empty-reduction helper test, empty-output helper
test and fused-graph regression fail with SEH 0xc0000094.
- After the fix, 160 helper combinations cover both operands, transpose
flags, empty K/M/N/batch and immediate/deferred offsets. The original
and mirrored fusion graphs match unfused execution.
- 444 helper/graph transformation tests pass; 17 GPU-only tests are
skipped. Scoped lintrunner and git diff --check pass.

The full graph transformation run also fails
SimplifiedLayerNormFusionPreservesIntegerToFloatCastEpsilon. Removing
this fix and rebuilding reproduces the same failure on the base
revision.

The local build uses MSVC 19.35 with CPU FP16 disabled and the existing
source-specific C4189 suppression for quantize_linear.cc and
sparse_attention.cc. CUDA execution was not tested.

### Description

Check the types required by `MatMulIntegerToFloat` before selecting the
no-output-Q MatMul rewrite:

- Both quantized operands must be INT8 or UINT8.
- The two scales and the original MatMul output must share the fused
operator's floating type.
- CPU requires FLOAT; DML's supported FLOAT16 path remains eligible.

Tests cover INT32 operands and supported 8-bit controls at opsets 13/19,
plus independent DQ scale/output types at opsets 23/25. CPU tests
compare execution results and operator selection. Separate graph-only
selector tests check CPU/DML precision rules; DML coverage here does not
execute its kernels.

### Motivation and Context

Fixes microsoft#33437.

INT32 `DequantizeLinear` inputs are legal, but the existing selector can
replace them with a fused operator that cannot consume INT32.

There is a related type mismatch after the independent CPU DQ
scale/output support in microsoft#32728: a legal opset-23 source can produce
FLOAT MatMul inputs using FLOAT16 scales. Fusion then binds the target's
single `T3` to incompatible scale/output types. Mixed FLOAT/FLOAT16
scales and two FLOAT16 scales with FLOAT output reproduce this failure.

The checks stay in the no-output-Q branch. CPU/DML enable that rewrite;
shared QDQ grouping for other EPs leaves it disabled.

### Validation

Windows x64, MSVC, Release CPU build based on main `a7a1172c`:

- The INT32 regression fails on original main. The two added
dtype/provider regressions also fail with the initial operand-only fix
(`a011e075`).
- Final `QDQTransformerTests.MatMul*`: all 15 passed.
- Complete `QDQTransformerTests.*`: all 173 passed, including those 15
focused tests.
- The original report's model now returns `[[11.0]]` with optimization
enabled.
- A local 144-case operand/parameter matrix and 8 independent
scale/output dtype combinations all return exact expected results with
the newly built Python module. The released 1.31.0 build has 64
operand-case failures and 3 dtype-case failures under optimization;
their unoptimized and pass-disabled controls are correct.
- Both changed files pass `lintrunner`; `git diff --check` is clean.

AI assistance was used for implementation, regression design, and
validation.

### Description
<!-- Describe your changes. -->

Acquire the pinned SDK with nuget.exe, verify its SHA1, and stage it in
a local CMake dependency mirror for Windows WebGPU plugin packaging. Add
focused regression tests.

### Motivation and Context
<!-- - Why is this change required? What problem does it solve?
- If it fixes an open issue, please link to the issue here. -->

Fix WebGPU plugin EP packaging pipeline.

---------

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>

…_context (microsoft#33694)

### Description
When `-p` is combined with `--compile_ep_context`,
`onnxruntime_perf_test` now enables profiling on the EP context compile
session too. The compile profile is written with a
`<profile_file>_compile` prefix, so it doesn't collide with the run
profile. The `--compile_ep_context` help text now mentions this.
Behavior without `-p` is unchanged.

### Motivation and Context
Previously only the run session had profiling enabled. EPs that decide
at compile time whether to include profiling support in the compiled
blob then fail at run time. With the OpenVINO EP on NPU,
`--compile_ep_context -p prof` fails with `Model was not compiled with
profiling enabled`.

Testing:
- CPU EP: with `-p`, both `prof_compile_*.json` and `prof_*.json` are
written. Without `-p`, no profile files are written, as before.
- OpenVINO plugin EP on an Intel NPU: a single `--compile_ep_context -p`
call now succeeds, and the run profile contains per-layer `OV::` events.
Before this change the same call failed with the error above.

### Description

Pass `-s ASYNCIFY_REMOVE=@onnxruntime/wasm/asyncify_remove.txt` to the
Asyncify builds (JSEP, and native WebGPU without JSPI), so that Asyncify
skips graph construction, ONNX schema and shape inference, and protobuf
parsing:

```
onnxruntime::Graph::*
onnxruntime::GraphViewer::*
onnx::*
google::protobuf::*
```

The JSPI build and the plain wasm build are unchanged.

### Motivation and Context

Addresses microsoft#33516; see also microsoft#26827.

`ASYNCIFY=1` instruments every function that makes an indirect call.
Graph resolution and ONNX shape inference make many of them, so they get
instrumented although they never reach an async import. In these builds
the async imports are:

- the JSEP and WebGPU readbacks;
- WebGPU adapter, device and pipeline creation;
- WebNN graph build and readback.

None of them is called from graph construction. The external data loader
is async only in JSPI builds.

The instrumentation roughly doubles some mid-size functions. WebKit's
optimizing wasm tier (OMG, [WebKit bug
304810](https://bugs.webkit.org/show_bug.cgi?id=304810)) needs several
GB of memory to compile them. The main one is
`onnxruntime::Graph::InferAndVerifyTypeMatch`:

| Build (1.30.0) | Size |
|---|---|
| Plain | 16.5 KB |
| JSEP | 30.6 KB |
| Native WebGPU | 28.8 KB |

I found it by padding function bodies past `JSC_maximumOMGCandidateCost`
so that OMG skips them, then bisecting. With `JSC_useOMGJIT=0` the
problem disappears completely.

Builds of this branch with the CI flags (no `--enable_wasm_profiling`).
The table shows peak RSS of the WebKit web content process for one
session create + `run()` of a 36 MB model with `executionProviders:
['wasm']`, using the page from microsoft#33516:

| Build | `.wasm` size | WebKit 18.2 | WebKit 27.2 |
|---|---|---|---|
| JSEP, `main` | 31.0 MB | 6.7-6.8 GB | 1.61 GB |
| JSEP, this PR | 29.7 MB | **1.9 GB** | **1.28 GB** |
| Native WebGPU (full types), `main` | 36.1 MB | 6.9-7.0 GB | 1.61 GB |
| Native WebGPU (full types), this PR | 34.8 MB | **1.9-2.0 GB** |
**1.33 GB** |
| Plain wasm (1.30.0 release, reference) | | 0.9 GB | 0.92 GB |

Chromium stays at ~0.7 GB either way. That was measured on the same
change applied to v1.30.0, which gave the same WebKit results as this
branch.

### Testing

- **Real recordings**: identical detections with and without the change
for 3 x 60 s in WebKit 18.2 and Chromium, and a 600 s recording in
Chromium (369 rows). The outputs also match the v1.30.0 builds.
- **WebGPU path**: this is where a wrongly removed function would break,
because an Asyncify unwind during readback would pass through it. A
small MLP ran fully on WebGPU (Chromium + SwiftShader) for 20 runs, each
with a GPU readback. Outputs were identical with and without the change
for both the JSEP build (40 `mapAsync`, JSEP kernels
Gemm/Relu/MatMul/Softmax) and the native WebGPU build (4 pipelines, 20
`mapAsync`).
- **Release flags**: both binaries shrink by 1.3 MB without
`--enable_wasm_profiling`, so the list matches even though the output
has no names section.
- **Not tested**: WebNN (not available in headless Chromium),
external-data models in the Asyncify builds, and real Safari. The WebKit
numbers come from Playwright's WPE builds on Linux x64. Real-device
reports in microsoft#26827 show the same pattern on iPadOS.

🤖 Generated with [Claude Code](https://claude.com/claude-code)

---------

Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>

…crosoft#33635)

### Description


Extend the existing K-parallel DP4A dispatch to narrow INT2/4/8
projections (`N <= 32`, `K >= 2048`), with FP32 accumulation of their
partial sums. Allow projections to share activation quantization and
subgroup-matrix input prepacking within one invocation.


The fixed 64×64 `DP4AMatMulNBitsProgram`, its dispatch, and its WGSL
shader are unchanged by this PR.


### Motivation and Context


Extract reusable kernel changes from microsoft#33370 so its QLoRA operator and
fused shaders can be reviewed separately. microsoft#33370 will be rebased after
this merges.


### Performance


RTX 5080, Windows, block size 32, graph capture enabled. GPU timestamp
medians include preparation and multiplication (two rounds, 100 replays
each, warm-up samples discarded):


| M × K × N | Weights / activations | D3D12, main → PR | Vulkan, main →
PR |
|---|---|---:|---:|

| 128 × 2048 × 32 | INT8 / FP16 | 47 → 10 µs | 52 → 14 µs |

| 512 × 4096 × 32 | INT8 / FP16 | 96 → 36 µs | 97.5 → 32 µs |

| 128 × 2048 × 4096 | INT4 / FP16 | 84.5 → 84 µs | 84 → 85 µs |

| 128 × 2048 × 4096 | INT4 / FP32 | 74 → 74 µs | 73.5 → 73 µs |


These measurements cover isolated GPU operators; timestamp resolution is
1 µs.


### Validation


- Windows Release build with built-in WebGPU, D3D12 and Vulkan; lint and
`git diff --check` passed.
- Provider regressions: 15 passed, five skipped (four Arm64/KleidiAI
cases and subgroup-matrix reuse on D3D12). All 28 QKV/MLP checks passed.
- All three shared-input tests passed with Vulkan, including
subgroup-matrix prepacking.
- Retained INT2/4/8 tests cover K-parallel dispatch thresholds, K tails,
16/32-column outputs, batching, zero points, bias, and FP32 inputs.
Shared-input tests also cover FP16 when supported by the device. Tests
specific to the removed tile variants are excluded.
- Dedicated FP16 INT2/4/8 regressions cover cancellation after partial
sums exceed the FP16 range, with the general FP32-accumulation option
disabled. They check device capabilities and disable CPU fallback. All
fail when the narrow-path FP32 override is removed and pass with it
restored.

Bumps [actions/setup-python](https://github.com/actions/setup-python) from 6.3.0 to 7.1.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/actions/setup-python/releases">actions/setup-python's releases</a>.</em></p> <blockquote> <h2>v7.1.0</h2> <h2>What's Changed</h2> <h3>Enhancements</h3> <ul> <li>Add <code>mirror</code> and <code>mirror-token</code> inputs for custom Python distribution sources by <a href="https://github.com/luhenry"><code>@luhenry</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1302">actions/setup-python#1302</a></li> <li>Improve error message clarity by <a href="https://github.com/v-lmvysakh"><code>@v-lmvysakh</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1351">actions/setup-python#1351</a></li> </ul> <h3>Dependency Upgrade</h3> <ul> <li>Upgrade browserslist from 4.28.2 to 4.28.9 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1353">actions/setup-python#1353</a></li> <li>Upgrade <code>@typescript-eslint/parser</code> from 8.62.0 to 8.70.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1343">actions/setup-python#1343</a></li> <li>Upgrade eslint-plugin-jest from 29.15.2 to 29.16.6 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1342">actions/setup-python#1342</a></li> <li>Upgrade <code>@vercel/ncc</code> from 0.44.0 to 0.45.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1357">actions/setup-python#1357</a></li> <li>Upgrade <code>@types/semver</code> from 7.7.1 to 7.8.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1359">actions/setup-python#1359</a></li> <li>Upgrade undici from 6.28.0 to 6.29.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1364">actions/setup-python#1364</a></li> <li>Upgrade ts-jest from 29.4.11 to 29.4.14 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1361">actions/setup-python#1361</a></li> <li>Upgrade brace-expansion from 5.0.9 to 5.0.12 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1365">actions/setup-python#1365</a></li> <li>Upgrade prettier from 3.8.4 to 3.9.9 and package.json from 7.0.0 to 7.1.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1363">actions/setup-python#1363</a></li> <li>Upgrade <code>@typescript-eslint/eslint-plugin</code> from 8.62.0 to 8.71.1 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1369">actions/setup-python#1369</a></li> <li>Upgrade actions/checkout from 7.0.0 to 7.0.1 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1345">actions/setup-python#1345</a></li> <li>Upgrade cache to 6.3.0 by <a href="https://github.com/v-HarithaVattikuti"><code>@v-HarithaVattikuti</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1370">actions/setup-python#1370</a></li> <li>Resolve Basic Validation audit failures by <a href="https://github.com/v-HarithaVattikuti"><code>@v-HarithaVattikuti</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1347">actions/setup-python#1347</a></li> <li>Resolve npm audit failures by <a href="https://github.com/v-HarithaVattikuti"><code>@v-HarithaVattikuti</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1350">actions/setup-python#1350</a></li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/luhenry"><code>@luhenry</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-python/pull/1302">actions/setup-python#1302</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/actions/setup-python/compare/v7.0.0...v7.1.0">https://github.com/actions/setup-python/compare/v7.0.0...v7.1.0</a></p> <h2>v7.0.0</h2> <h2>What's Changed</h2> <h3>Enhancements</h3> <ul> <li>Migrate to ESM and upgrade dependencies by <a href="https://github.com/priyagupta108"><code>@priyagupta108</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1330">actions/setup-python#1330</a></li> <li>Pin SHA commits and update docs with latest versions by <a href="https://github.com/HarithaVattikuti"><code>@HarithaVattikuti</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1338">actions/setup-python#1338</a></li> <li>Remove the pip-install input by <a href="https://github.com/gowridurgad"><code>@gowridurgad</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1336">actions/setup-python#1336</a></li> </ul> <h3>Bug Fix</h3> <ul> <li>Fix to Classify stderr warning messages as warnings instead of errors in annotations by <a href="https://github.com/lmvysakh"><code>@lmvysakh</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1335">actions/setup-python#1335</a></li> <li>Validate and retry manifest fetch to prevent silent failures by <a href="https://github.com/priyagupta108"><code>@priyagupta108</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1332">actions/setup-python#1332</a></li> </ul> <h3>Dependency Upgrade</h3> <ul> <li>Bump certifi from 2020.6.20 to 2024.7.4 in /<strong>tests</strong>/data by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1328">actions/setup-python#1328</a></li> <li>Remove EOL Python versions and Bumps numpy text fixture by <a href="https://github.com/priya-kinthali"><code>@priya-kinthali</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1333">actions/setup-python#1333</a></li> <li>Upgrade <code>@actions/cache</code> to 6.2.0 by <a href="https://github.com/philip-gai"><code>@philip-gai</code></a> in <a href="https://redirect.github.com/actions/setup-python/pull/1337">actions/setup-python#1337</a></li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/lmvysakh"><code>@lmvysakh</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-python/pull/1335">actions/setup-python#1335</a></li> <li><a href="https://github.com/philip-gai"><code>@philip-gai</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-python/pull/1337">actions/setup-python#1337</a></li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/actions/setup-python/commit/6d4fd22b20465ccc0f7354476588e8df7c9ca0e0"><code>6d4fd22</code></a> Cache upgrade to 6.3.0 (<a href="https://redirect.github.com/actions/setup-python/issues/1370">#1370</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/ec52d0af729a7c50ced4261d17a07916f43f5b8e"><code>ec52d0a</code></a> Bump <code>@typescript-eslint/eslint-plugin</code> from 8.62.0 to 8.71.1 (<a href="https://redirect.github.com/actions/setup-python/issues/1369">#1369</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/ff73b2463e2f3baa703f830da214b8dfeeaeccf8"><code>ff73b24</code></a> Bump prettier from 3.8.4 to 3.9.9 and package.json from 7.0.0 to 7.1.0 (<a href="https://redirect.github.com/actions/setup-python/issues/1363">#1363</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/0e40890053525508c059c61932a6b8614f9e95db"><code>0e40890</code></a> Bump brace-expansion from 5.0.9 to 5.0.12 (<a href="https://redirect.github.com/actions/setup-python/issues/1365">#1365</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/3892123fbe74688ccc83ec7c465dc688359e5199"><code>3892123</code></a> Bump ts-jest from 29.4.11 to 29.4.14 (<a href="https://redirect.github.com/actions/setup-python/issues/1361">#1361</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/660965736c4aecc62797ea07d351a3c259f14660"><code>6609657</code></a> Bump undici from 6.28.0 to 6.29.0 (<a href="https://redirect.github.com/actions/setup-python/issues/1364">#1364</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/e1be392b26fb1917a7b2c455817e4b4dad6544ce"><code>e1be392</code></a> Bump <code>@types/semver</code> from 7.7.1 to 7.8.0 (<a href="https://redirect.github.com/actions/setup-python/issues/1359">#1359</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/06da6279cdbca41027908073e81a4544dc79c06b"><code>06da627</code></a> Bump <code>@vercel/ncc</code> from 0.44.0 to 0.45.0 (<a href="https://redirect.github.com/actions/setup-python/issues/1357">#1357</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/af9bcc7548695e66d75709de6f29e337624b8de8"><code>af9bcc7</code></a> Bump eslint-plugin-jest from 29.15.2 to 29.16.6 (<a href="https://redirect.github.com/actions/setup-python/issues/1342">#1342</a>)</li> <li><a href="https://github.com/actions/setup-python/commit/7aeabeba5501120d873c50398519dbfd0657031c"><code>7aeabeb</code></a> Bump <code>@typescript-eslint/parser</code> from 8.62.0 to 8.70.0 (<a href="https://redirect.github.com/actions/setup-python/issues/1343">#1343</a>)</li> <li>Additional commits viewable in <a href="https://github.com/actions/setup-python/compare/ece7cb06caefa5fff74198d8649806c4678c61a1...6d4fd22b20465ccc0f7354476588e8df7c9ca0e0">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
…33610) Bumps [fast-uri](https://github.com/fastify/fast-uri) from 3.1.7 to 3.1.9. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/fastify/fast-uri/releases">fast-uri's releases</a>.</em></p> <blockquote> <h2>v3.1.9</h2> <h2>Security</h2> <p>This security release fixes four URI parsing and normalization vulnerabilities in fast-uri 3.x. Applications that process untrusted URI input should upgrade to v3.1.9.</p> <ul> <li><strong>Medium — URI scheme spoofing through percent-encoded schemes</strong> (<a href="https://github.com/fastify/fast-uri/security/advisories/GHSA-w74x-v6f9-j3xg">GHSA-w74x-v6f9-j3xg</a>, CVE-2026-110306): percent-encoded scheme input is now rejected instead of being decoded into a live scheme.</li> <li><strong>Medium — Host confusion during domain-host canonicalization</strong> (<a href="https://github.com/fastify/fast-uri/security/advisories/GHSA-wjr9-j795-jxcr">GHSA-wjr9-j795-jxcr</a>, CVE-2026-110180): malformed domain hosts containing ambiguous delimiters or stripped control characters are now rejected instead of being silently rewritten.</li> <li><strong>Low — Incorrect relative-reference normalization</strong> (<a href="https://github.com/fastify/fast-uri/security/advisories/GHSA-xhq7-xmqj-769h">GHSA-xhq7-xmqj-769h</a>, CVE-2026-110095): dot-segment removal now preserves the resolution semantics of relative references.</li> <li><strong>Low — Scheme injection in suffix references</strong> (<a href="https://github.com/fastify/fast-uri/security/advisories/GHSA-333x-w4r6-6crp">GHSA-333x-w4r6-6crp</a>, CVE-2026-110725): first-segment colons in path-only suffix references are now escaped so the output is not reparsed as a scheme.</li> </ul> <p>Upgrade with:</p> <pre lang="sh"><code>npm install fast-uri@3.1.9 </code></pre> <p>Thanks to <a href="https://github.com/zekth"><code>@zekth</code></a> for reporting the scheme, host, and relative-reference issues, and to <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> for finding the suffix-reference issue and reviewing the remediations.</p> <h2>What's Changed</h2> <ul> <li>ci: enable trusted publishing releases (v3.x) by <a href="https://github.com/mcollina"><code>@mcollina</code></a> in <a href="https://redirect.github.com/fastify/fast-uri/pull/229">fastify/fast-uri#229</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/fastify/fast-uri/compare/v3.1.8...v3.1.9">https://github.com/fastify/fast-uri/compare/v3.1.8...v3.1.9</a></p> <h2>v3.1.8</h2> <h2>⚠️ Security Warning</h2> <p>This security release fixes the following medium-severity security advisory:</p> <ul> <li><a href="https://github.com/fastify/fast-uri/security/advisories/GHSA-hrr3-gc8f-f4qj">GHSA-hrr3-gc8f-f4qj</a> — inconsistent host case normalization via percent-encoded octets</li> </ul> <p>Users of the v3.x release line should upgrade to v3.1.8.</p> <p><strong>Full Changelog</strong>: <a href="https://github.com/fastify/fast-uri/compare/v3.1.7...v3.1.8">https://github.com/fastify/fast-uri/compare/v3.1.7...v3.1.8</a></p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/fastify/fast-uri/commit/0def70338a0fa2f12a10c83ae8eafc2139ae9a07"><code>0def703</code></a> Bumped v3.1.9</li> <li><a href="https://github.com/fastify/fast-uri/commit/a1d0da2f5c703244027c1b204c1aebd0516da338"><code>a1d0da2</code></a> test: generate only relative path references</li> <li><a href="https://github.com/fastify/fast-uri/commit/9eb8759a9825c046f57f7f695f1944bc39b88abd"><code>9eb8759</code></a> fix: preserve relative paths in suffix and relative resolution</li> <li><a href="https://github.com/fastify/fast-uri/commit/54c30f75891b74e5a4393b44be9ea7ba43dd1e4b"><code>54c30f7</code></a> docs: note suffix-reference authority ambiguity</li> <li><a href="https://github.com/fastify/fast-uri/commit/39e6493c1356f30a0084171627eb266786e1620e"><code>39e6493</code></a> fix: escape a first-segment colon in suffix references</li> <li><a href="https://github.com/fastify/fast-uri/commit/745183c1d9d98d113bed8a57bb1c9ceaf0147b7a"><code>745183c</code></a> test: cover first-segment colon in suffix references</li> <li><a href="https://github.com/fastify/fast-uri/commit/ddfc6a51122dfce0365655f04479fc3adb7f6b3c"><code>ddfc6a5</code></a> fix(SEC-03): reject non reg-name characters in domain hosts</li> <li><a href="https://github.com/fastify/fast-uri/commit/d86a8d29f45187819dac2d4fe171c35e3e488264"><code>d86a8d2</code></a> fix: keep a colon-first segment behind "./" in relative normalization</li> <li><a href="https://github.com/fastify/fast-uri/commit/eb483b5da2580bdecb8af644bbfee878d5424850"><code>eb483b5</code></a> test: cover colon-first relative references in normalization</li> <li><a href="https://github.com/fastify/fast-uri/commit/b110a3571c37dfcf9d1c72ce2e2e178c78d1a424"><code>b110a35</code></a> fix(SEC-02): preserve meaning of relative references during normalization</li> <li>Additional commits viewable in <a href="https://github.com/fastify/fast-uri/compare/v3.1.7...v3.1.9">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for fast-uri since your current version.</p> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) You can disable automated security fix PRs for this repo from the [Security Alerts page](https://github.com/microsoft/onnxruntime/network/alerts). </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>

…icrosoft#33639)

### Description

The subgroup matrix MatMul kernel loads A and B straight from global
memory with one subgroup per K split, so this PR adds a path where a
workgroup of subgroups copies a K slice of A and B into shared memory
and loads its subgroup matrices from there. On NVIDIA a 4x4 grid of
subgroups stages K slices 64 deep and computes a 128x128 output tile for
large problems and a 64x64 tile otherwise, while small problems keep the
existing split K tiling because it fills the GPU better there, and each
tiling is checked against the device limits with the existing tiling as
the fallback. The tile sizes and the K depth were measured in ORT on an
RTX 5080 and an RTX 4070, and since the path is selected for NVIDIA
only, other vendors are unchanged.

### Motivation and Context

Prefill speedup over main for the onnx-community models on Linux with
Vulkan, P50 of 100 runs with `onnxruntime_perf_test`, averaged over five
rounds:

| Model, prompt tokens | RTX 5080 | RTX 4070 |
|---|---:|---:|
| Llama-3.2-1B-Instruct fp16, 512 | 10.6% | 25.3% |
| Llama-3.2-1B-Instruct fp16, 1024 | 5.6% | 21.0% |
| Qwen3-0.6B fp16, 512 | 3.1% | 10.5% |
| Qwen3-0.6B fp16, 1024 | -0.6% | 13.7% |
| gemma-3-270m-it fp16, 512 | 6.3% | 7.2% |
| gemma-3-270m-it fp16, 1024 | 2.8% | 9.4% |
| Llama-3.2-1B-Instruct q4f16, 512 | 5.7% | 11.5% |
| Llama-3.2-1B-Instruct q4f16, 1024 | 5.4% | 4.9% |
| Qwen3-0.6B q4f16, 512 | 3.1% | 4.5% |
| Qwen3-0.6B q4f16, 1024 | 0.3% | 6.4% |
| Geometric mean | 4.2% | 11.3% |

The q4f16 models gain because their `lm_head` MatMul is FP16.
Bumps [reviewdog/action-shellcheck](https://github.com/reviewdog/action-shellcheck) from 1.32.1 to 1.34.1. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/reviewdog/action-shellcheck/releases">reviewdog/action-shellcheck's releases</a>.</em></p> <blockquote> <h2>Release v1.34.1</h2> <h2>What's Changed</h2> <ul> <li>fix: quote the composite action script path by <a href="https://github.com/dajiaohuang"><code>@dajiaohuang</code></a> in <a href="https://redirect.github.com/reviewdog/action-shellcheck/pull/106">reviewdog/action-shellcheck#106</a></li> <li>fix: fail when shellcheck installation fails by <a href="https://github.com/dajiaohuang"><code>@dajiaohuang</code></a> in <a href="https://redirect.github.com/reviewdog/action-shellcheck/pull/105">reviewdog/action-shellcheck#105</a></li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/dajiaohuang"><code>@dajiaohuang</code></a> made their first contribution in <a href="https://redirect.github.com/reviewdog/action-shellcheck/pull/106">reviewdog/action-shellcheck#106</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/reviewdog/action-shellcheck/compare/v1.34.0...v1.34.1">https://github.com/reviewdog/action-shellcheck/compare/v1.34.0...v1.34.1</a></p> <h2>Release v1.34.0</h2> <h2>What's Changed</h2> <ul> <li>chore(deps): update reviewdog/reviewdog to 0.21.2 by <a href="https://github.com/github-actions"><code>@github-actions</code></a>[bot] in <a href="https://redirect.github.com/reviewdog/action-shellcheck/pull/104">reviewdog/action-shellcheck#104</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/reviewdog/action-shellcheck/compare/v1.33.0...v1.34.0">https://github.com/reviewdog/action-shellcheck/compare/v1.33.0...v1.34.0</a></p> <h2>Release v1.33.0</h2> <h2>What's Changed</h2> <ul> <li>chore(deps): update reviewdog/reviewdog to 0.21.1 by <a href="https://github.com/github-actions"><code>@github-actions</code></a>[bot] in <a href="https://redirect.github.com/reviewdog/action-shellcheck/pull/103">reviewdog/action-shellcheck#103</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/reviewdog/action-shellcheck/compare/v1.32.1...v1.33.0">https://github.com/reviewdog/action-shellcheck/compare/v1.32.1...v1.33.0</a></p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/d0b8d5fd7fad6afdb6e1b6ce1778892be4d1f427"><code>d0b8d5f</code></a> Merge pull request <a href="https://redirect.github.com/reviewdog/action-shellcheck/issues/105">#105</a> from dajiaohuang/fix-shellcheck-install-failures</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/4be16f57c06c0e06972b5a54191b94450c17f440"><code>4be16f5</code></a> Merge pull request <a href="https://redirect.github.com/reviewdog/action-shellcheck/issues/106">#106</a> from dajiaohuang/fix-action-path-spaces</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/e3349979924920c7cf5c5303031391ef430e753d"><code>e334997</code></a> fix: quote the composite action script path</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/a9174c8ca1d4b0e1979b6e002d564020273c4e98"><code>a9174c8</code></a> fix: fail when shellcheck installation fails</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/0a90156c6e0553996a217f0a9e09be6b0f6bee4c"><code>0a90156</code></a> Merge pull request <a href="https://redirect.github.com/reviewdog/action-shellcheck/issues/104">#104</a> from reviewdog/depup/reviewdog/reviewdog</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/01c7a4ffc0fca3fd9b106e20c055a92ad733f350"><code>01c7a4f</code></a> chore(deps): update reviewdog/reviewdog to 0.21.2</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/a94d585085f1f5215ae65f4de34e7bbd0523d550"><code>a94d585</code></a> Merge pull request <a href="https://redirect.github.com/reviewdog/action-shellcheck/issues/103">#103</a> from reviewdog/depup/reviewdog/reviewdog</li> <li><a href="https://github.com/reviewdog/action-shellcheck/commit/145c1d86cd3fb9febbf0bb01f452d44deacf4aab"><code>145c1d8</code></a> chore(deps): update reviewdog/reviewdog to 0.21.1</li> <li>See full diff in <a href="https://github.com/reviewdog/action-shellcheck/compare/0722bbdb0d47f04c1b53b8734d2422ac63a45ec6...d0b8d5fd7fad6afdb6e1b6ce1778892be4d1f427">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
Bumps the codeql group with 4 updates:
[github/codeql-action/init](https://github.com/github/codeql-action),
[github/codeql-action/autobuild](https://github.com/github/codeql-action),
[github/codeql-action/analyze](https://github.com/github/codeql-action)
and
[github/codeql-action/upload-sarif](https://github.com/github/codeql-action).

Updates `github/codeql-action/init` from 4.39.0 to 4.39.1
<details>
<summary>Release notes</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/releases">github/codeql-action/init's
releases</a>.</em></p>
<blockquote>
<h2>v4.39.1</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
</blockquote>
</details>
<details>
<summary>Changelog</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/blob/main/CHANGELOG.md">github/codeql-action/init's
changelog</a>.</em></p>
<blockquote>
<h1>CodeQL Action Changelog</h1>
<p>See the <a
href="https://github.com/github/codeql-action/releases">releases
page</a> for the relevant changes to the CodeQL CLI and language
packs.</p>
<h2>[UNRELEASED]</h2>
<p>No user facing changes.</p>
<h2>4.39.1 - 21 Oct 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
<h2>4.39.0 - 15 Oct 2026</h2>
<ul>
<li><em>Breaking change</em>: Bump the minimum required CodeQL bundle
version to 2.20.7. <a
href="https://redirect.github.com/github/codeql-action/pull/4205">#4205</a></li>
<li>The <code>codeql-action/analyze</code> step now validates that a
correct argument for the <code>checkout_path</code> input has been
provided. The <code>checkout_path</code> input must be set to the path
where the repository that is being analyzed is checked out at on the
runner, if that path is something other than the workspace root. If the
path does not point to a repository checkout or is different from the
path that was used by <code>codeql-action/init</code>, then the CodeQL
Action now produces a warning. <a
href="https://redirect.github.com/github/codeql-action/pull/4148">#4148</a></li>
<li>Resolved an issue with third-party caching implementations that
prevented caches from being restored correctly. <a
href="https://redirect.github.com/github/codeql-action/pull/4206">#4206</a></li>
<li>The <code>codeql-action/start-proxy</code> step that is used in Code
Scanning Default Setup now finds CodeQL releases using the same logic as
<code>codeql-action/init</code>. This primarily benefits customers who
are using GitHub instances other than <code>github.com</code> where the
<code>codeql-action/start-proxy</code> step may previously have been
unable to locate recent releases and ended up using outdated versions of
the private registry authentication proxy as a result. <a
href="https://redirect.github.com/github/codeql-action/pull/4198">#4198</a></li>
</ul>
<h2>4.38.3 - 08 Oct 2026</h2>
<ul>
<li><em>Upcoming breaking change</em>: CodeQL version 2.21.2 and earlier
were discontinued on 24 September 2026 alongside GitHub Enterprise
Server 3.17, and will be unsupported by the next minor release of the
CodeQL Action. Added a deprecation warning for customers using these
versions of CodeQL. <a
href="https://redirect.github.com/github/codeql-action/pull/4188">#4188</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.2">2.27.2</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4203">#4203</a></li>
<li>Fixed a bug where the decision of whether to use a per-language
bundle did not account for custom configurations that reference queries
outside of compiled CodeQL packs. This issue was caught during internal
testing and did not affect any customer repositories. We will resume the
roll out of per-language bundles in the coming weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4184">#4184</a></li>
</ul>
<h2>4.38.2 - 24 Sept 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.1">2.27.1</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4160">#4160</a></li>
</ul>
<h2>4.38.1 - 18 Sept 2026</h2>
<ul>
<li>The CodeQL Action now has experimental support for CodeQL releases
for which per-language bundles are available. Per-language bundles
support analysis for a single language and are therefore smaller than
the combined bundles that allow analysis for all supported languages. As
a result, per-language bundles take up less space on disk and are faster
to download. We expect to roll this change out to everyone in the coming
weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4146">#4146</a></li>
</ul>
<h2>4.38.0 - 09 Sept 2026</h2>
<ul>
<li>On GitHub-hosted runners, the CodeQL Action now deletes unused
CodeQL bundles from the toolcache before downloading a different bundle,
which frees up disk space for the analysis. We expect to roll this
change out to everyone in September. <a
href="https://redirect.github.com/github/codeql-action/pull/4124">#4124</a></li>
<li>The CodeQL Action now supports CodeQL releases that are compatible
with Linux Arm64 and downloads the native <code>linux-arm64</code>
CodeQL bundle when available. <a
href="https://redirect.github.com/github/codeql-action/pull/4072">#4072</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.0">2.27.0</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4129">#4129</a></li>
</ul>
<h2>4.37.9 - 26 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.4">2.26.4</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4106">#4106</a></li>
</ul>
<h2>4.37.8 - 21 Aug 2026</h2>
<p>No user facing changes.</p>
<h2>4.37.7 - 13 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.3">2.26.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4085">#4085</a></li>
</ul>
<!-- raw HTML omitted -->
</blockquote>
<p>... (truncated)</p>
</details>
<details>
<summary>Commits</summary>
<ul>
<li><a
href="https://github.com/github/codeql-action/commit/9b3254085494b55a0f7c4c2b3d2d52cc712ce370"><code>9b32540</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4257">#4257</a>
from github/update-v4.39.1-c5a2f4b0f</li>
<li><a
href="https://github.com/github/codeql-action/commit/b5e1ed9574dcfa81c88c318140f3b3e5c199bfb3"><code>b5e1ed9</code></a>
Trigger workflows</li>
<li><a
href="https://github.com/github/codeql-action/commit/20f5ec39109073afe1789b098456b2be0164f4ee"><code>20f5ec3</code></a>
Update changelog for v4.39.1</li>
<li><a
href="https://github.com/github/codeql-action/commit/c5a2f4b0fe28ca06eaaeb86fb05a5f612ae293f9"><code>c5a2f4b</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4245">#4245</a>
from github/henrymercer/graduate-overlay-trap-caching</li>
<li><a
href="https://github.com/github/codeql-action/commit/61a5a80dd98ad1b9679010141a46cace51065761"><code>61a5a80</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4256">#4256</a>
from github/update-bundle/codeql-bundle-v2.27.3</li>
<li><a
href="https://github.com/github/codeql-action/commit/3dd33f8b69588bd9591684b2dca169eb612f5ed5"><code>3dd33f8</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4249">#4249</a>
from github/mbg/upload-improvements-for-4223</li>
<li><a
href="https://github.com/github/codeql-action/commit/b96e3390db93dc46c2c3753a94b87c0d734b0b61"><code>b96e339</code></a>
Change comment for <code>getConfig</code> call in
<code>upload-sarif</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/7fa45180db8d657b23ded3636b5d8583aec6ddfe"><code>7fa4518</code></a>
Use <code>shouldSkipSarifUpload</code> in
<code>analyze-action.ts</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/a69c7cb332d56f616fcadef002884523c71e8d1c"><code>a69c7cb</code></a>
Document that setting the env vars to <code>false</code> takes
precedence</li>
<li><a
href="https://github.com/github/codeql-action/commit/74ddcd9f65683791ab07eccd074b4ba145d89ea6"><code>74ddcd9</code></a>
Fix typo in comment</li>
<li>Additional commits viewable in <a
href="https://github.com/github/codeql-action/compare/6f2ac81f5cd81fe351a197ba0b00d91d03cd2aee...9b3254085494b55a0f7c4c2b3d2d52cc712ce370">compare
view</a></li>
</ul>
</details>
<br />

Updates `github/codeql-action/autobuild` from 4.39.0 to 4.39.1
<details>
<summary>Release notes</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/releases">github/codeql-action/autobuild's
releases</a>.</em></p>
<blockquote>
<h2>v4.39.1</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
</blockquote>
</details>
<details>
<summary>Changelog</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/blob/main/CHANGELOG.md">github/codeql-action/autobuild's
changelog</a>.</em></p>
<blockquote>
<h1>CodeQL Action Changelog</h1>
<p>See the <a
href="https://github.com/github/codeql-action/releases">releases
page</a> for the relevant changes to the CodeQL CLI and language
packs.</p>
<h2>[UNRELEASED]</h2>
<p>No user facing changes.</p>
<h2>4.39.1 - 21 Oct 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
<h2>4.39.0 - 15 Oct 2026</h2>
<ul>
<li><em>Breaking change</em>: Bump the minimum required CodeQL bundle
version to 2.20.7. <a
href="https://redirect.github.com/github/codeql-action/pull/4205">#4205</a></li>
<li>The <code>codeql-action/analyze</code> step now validates that a
correct argument for the <code>checkout_path</code> input has been
provided. The <code>checkout_path</code> input must be set to the path
where the repository that is being analyzed is checked out at on the
runner, if that path is something other than the workspace root. If the
path does not point to a repository checkout or is different from the
path that was used by <code>codeql-action/init</code>, then the CodeQL
Action now produces a warning. <a
href="https://redirect.github.com/github/codeql-action/pull/4148">#4148</a></li>
<li>Resolved an issue with third-party caching implementations that
prevented caches from being restored correctly. <a
href="https://redirect.github.com/github/codeql-action/pull/4206">#4206</a></li>
<li>The <code>codeql-action/start-proxy</code> step that is used in Code
Scanning Default Setup now finds CodeQL releases using the same logic as
<code>codeql-action/init</code>. This primarily benefits customers who
are using GitHub instances other than <code>github.com</code> where the
<code>codeql-action/start-proxy</code> step may previously have been
unable to locate recent releases and ended up using outdated versions of
the private registry authentication proxy as a result. <a
href="https://redirect.github.com/github/codeql-action/pull/4198">#4198</a></li>
</ul>
<h2>4.38.3 - 08 Oct 2026</h2>
<ul>
<li><em>Upcoming breaking change</em>: CodeQL version 2.21.2 and earlier
were discontinued on 24 September 2026 alongside GitHub Enterprise
Server 3.17, and will be unsupported by the next minor release of the
CodeQL Action. Added a deprecation warning for customers using these
versions of CodeQL. <a
href="https://redirect.github.com/github/codeql-action/pull/4188">#4188</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.2">2.27.2</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4203">#4203</a></li>
<li>Fixed a bug where the decision of whether to use a per-language
bundle did not account for custom configurations that reference queries
outside of compiled CodeQL packs. This issue was caught during internal
testing and did not affect any customer repositories. We will resume the
roll out of per-language bundles in the coming weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4184">#4184</a></li>
</ul>
<h2>4.38.2 - 24 Sept 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.1">2.27.1</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4160">#4160</a></li>
</ul>
<h2>4.38.1 - 18 Sept 2026</h2>
<ul>
<li>The CodeQL Action now has experimental support for CodeQL releases
for which per-language bundles are available. Per-language bundles
support analysis for a single language and are therefore smaller than
the combined bundles that allow analysis for all supported languages. As
a result, per-language bundles take up less space on disk and are faster
to download. We expect to roll this change out to everyone in the coming
weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4146">#4146</a></li>
</ul>
<h2>4.38.0 - 09 Sept 2026</h2>
<ul>
<li>On GitHub-hosted runners, the CodeQL Action now deletes unused
CodeQL bundles from the toolcache before downloading a different bundle,
which frees up disk space for the analysis. We expect to roll this
change out to everyone in September. <a
href="https://redirect.github.com/github/codeql-action/pull/4124">#4124</a></li>
<li>The CodeQL Action now supports CodeQL releases that are compatible
with Linux Arm64 and downloads the native <code>linux-arm64</code>
CodeQL bundle when available. <a
href="https://redirect.github.com/github/codeql-action/pull/4072">#4072</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.0">2.27.0</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4129">#4129</a></li>
</ul>
<h2>4.37.9 - 26 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.4">2.26.4</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4106">#4106</a></li>
</ul>
<h2>4.37.8 - 21 Aug 2026</h2>
<p>No user facing changes.</p>
<h2>4.37.7 - 13 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.3">2.26.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4085">#4085</a></li>
</ul>
<!-- raw HTML omitted -->
</blockquote>
<p>... (truncated)</p>
</details>
<details>
<summary>Commits</summary>
<ul>
<li><a
href="https://github.com/github/codeql-action/commit/9b3254085494b55a0f7c4c2b3d2d52cc712ce370"><code>9b32540</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4257">#4257</a>
from github/update-v4.39.1-c5a2f4b0f</li>
<li><a
href="https://github.com/github/codeql-action/commit/b5e1ed9574dcfa81c88c318140f3b3e5c199bfb3"><code>b5e1ed9</code></a>
Trigger workflows</li>
<li><a
href="https://github.com/github/codeql-action/commit/20f5ec39109073afe1789b098456b2be0164f4ee"><code>20f5ec3</code></a>
Update changelog for v4.39.1</li>
<li><a
href="https://github.com/github/codeql-action/commit/c5a2f4b0fe28ca06eaaeb86fb05a5f612ae293f9"><code>c5a2f4b</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4245">#4245</a>
from github/henrymercer/graduate-overlay-trap-caching</li>
<li><a
href="https://github.com/github/codeql-action/commit/61a5a80dd98ad1b9679010141a46cace51065761"><code>61a5a80</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4256">#4256</a>
from github/update-bundle/codeql-bundle-v2.27.3</li>
<li><a
href="https://github.com/github/codeql-action/commit/3dd33f8b69588bd9591684b2dca169eb612f5ed5"><code>3dd33f8</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4249">#4249</a>
from github/mbg/upload-improvements-for-4223</li>
<li><a
href="https://github.com/github/codeql-action/commit/b96e3390db93dc46c2c3753a94b87c0d734b0b61"><code>b96e339</code></a>
Change comment for <code>getConfig</code> call in
<code>upload-sarif</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/7fa45180db8d657b23ded3636b5d8583aec6ddfe"><code>7fa4518</code></a>
Use <code>shouldSkipSarifUpload</code> in
<code>analyze-action.ts</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/a69c7cb332d56f616fcadef002884523c71e8d1c"><code>a69c7cb</code></a>
Document that setting the env vars to <code>false</code> takes
precedence</li>
<li><a
href="https://github.com/github/codeql-action/commit/74ddcd9f65683791ab07eccd074b4ba145d89ea6"><code>74ddcd9</code></a>
Fix typo in comment</li>
<li>Additional commits viewable in <a
href="https://github.com/github/codeql-action/compare/6f2ac81f5cd81fe351a197ba0b00d91d03cd2aee...9b3254085494b55a0f7c4c2b3d2d52cc712ce370">compare
view</a></li>
</ul>
</details>
<br />

Updates `github/codeql-action/analyze` from 4.39.0 to 4.39.1
<details>
<summary>Release notes</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/releases">github/codeql-action/analyze's
releases</a>.</em></p>
<blockquote>
<h2>v4.39.1</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
</blockquote>
</details>
<details>
<summary>Changelog</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/blob/main/CHANGELOG.md">github/codeql-action/analyze's
changelog</a>.</em></p>
<blockquote>
<h1>CodeQL Action Changelog</h1>
<p>See the <a
href="https://github.com/github/codeql-action/releases">releases
page</a> for the relevant changes to the CodeQL CLI and language
packs.</p>
<h2>[UNRELEASED]</h2>
<p>No user facing changes.</p>
<h2>4.39.1 - 21 Oct 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
<h2>4.39.0 - 15 Oct 2026</h2>
<ul>
<li><em>Breaking change</em>: Bump the minimum required CodeQL bundle
version to 2.20.7. <a
href="https://redirect.github.com/github/codeql-action/pull/4205">#4205</a></li>
<li>The <code>codeql-action/analyze</code> step now validates that a
correct argument for the <code>checkout_path</code> input has been
provided. The <code>checkout_path</code> input must be set to the path
where the repository that is being analyzed is checked out at on the
runner, if that path is something other than the workspace root. If the
path does not point to a repository checkout or is different from the
path that was used by <code>codeql-action/init</code>, then the CodeQL
Action now produces a warning. <a
href="https://redirect.github.com/github/codeql-action/pull/4148">#4148</a></li>
<li>Resolved an issue with third-party caching implementations that
prevented caches from being restored correctly. <a
href="https://redirect.github.com/github/codeql-action/pull/4206">#4206</a></li>
<li>The <code>codeql-action/start-proxy</code> step that is used in Code
Scanning Default Setup now finds CodeQL releases using the same logic as
<code>codeql-action/init</code>. This primarily benefits customers who
are using GitHub instances other than <code>github.com</code> where the
<code>codeql-action/start-proxy</code> step may previously have been
unable to locate recent releases and ended up using outdated versions of
the private registry authentication proxy as a result. <a
href="https://redirect.github.com/github/codeql-action/pull/4198">#4198</a></li>
</ul>
<h2>4.38.3 - 08 Oct 2026</h2>
<ul>
<li><em>Upcoming breaking change</em>: CodeQL version 2.21.2 and earlier
were discontinued on 24 September 2026 alongside GitHub Enterprise
Server 3.17, and will be unsupported by the next minor release of the
CodeQL Action. Added a deprecation warning for customers using these
versions of CodeQL. <a
href="https://redirect.github.com/github/codeql-action/pull/4188">#4188</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.2">2.27.2</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4203">#4203</a></li>
<li>Fixed a bug where the decision of whether to use a per-language
bundle did not account for custom configurations that reference queries
outside of compiled CodeQL packs. This issue was caught during internal
testing and did not affect any customer repositories. We will resume the
roll out of per-language bundles in the coming weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4184">#4184</a></li>
</ul>
<h2>4.38.2 - 24 Sept 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.1">2.27.1</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4160">#4160</a></li>
</ul>
<h2>4.38.1 - 18 Sept 2026</h2>
<ul>
<li>The CodeQL Action now has experimental support for CodeQL releases
for which per-language bundles are available. Per-language bundles
support analysis for a single language and are therefore smaller than
the combined bundles that allow analysis for all supported languages. As
a result, per-language bundles take up less space on disk and are faster
to download. We expect to roll this change out to everyone in the coming
weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4146">#4146</a></li>
</ul>
<h2>4.38.0 - 09 Sept 2026</h2>
<ul>
<li>On GitHub-hosted runners, the CodeQL Action now deletes unused
CodeQL bundles from the toolcache before downloading a different bundle,
which frees up disk space for the analysis. We expect to roll this
change out to everyone in September. <a
href="https://redirect.github.com/github/codeql-action/pull/4124">#4124</a></li>
<li>The CodeQL Action now supports CodeQL releases that are compatible
with Linux Arm64 and downloads the native <code>linux-arm64</code>
CodeQL bundle when available. <a
href="https://redirect.github.com/github/codeql-action/pull/4072">#4072</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.0">2.27.0</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4129">#4129</a></li>
</ul>
<h2>4.37.9 - 26 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.4">2.26.4</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4106">#4106</a></li>
</ul>
<h2>4.37.8 - 21 Aug 2026</h2>
<p>No user facing changes.</p>
<h2>4.37.7 - 13 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.3">2.26.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4085">#4085</a></li>
</ul>
<!-- raw HTML omitted -->
</blockquote>
<p>... (truncated)</p>
</details>
<details>
<summary>Commits</summary>
<ul>
<li><a
href="https://github.com/github/codeql-action/commit/9b3254085494b55a0f7c4c2b3d2d52cc712ce370"><code>9b32540</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4257">#4257</a>
from github/update-v4.39.1-c5a2f4b0f</li>
<li><a
href="https://github.com/github/codeql-action/commit/b5e1ed9574dcfa81c88c318140f3b3e5c199bfb3"><code>b5e1ed9</code></a>
Trigger workflows</li>
<li><a
href="https://github.com/github/codeql-action/commit/20f5ec39109073afe1789b098456b2be0164f4ee"><code>20f5ec3</code></a>
Update changelog for v4.39.1</li>
<li><a
href="https://github.com/github/codeql-action/commit/c5a2f4b0fe28ca06eaaeb86fb05a5f612ae293f9"><code>c5a2f4b</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4245">#4245</a>
from github/henrymercer/graduate-overlay-trap-caching</li>
<li><a
href="https://github.com/github/codeql-action/commit/61a5a80dd98ad1b9679010141a46cace51065761"><code>61a5a80</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4256">#4256</a>
from github/update-bundle/codeql-bundle-v2.27.3</li>
<li><a
href="https://github.com/github/codeql-action/commit/3dd33f8b69588bd9591684b2dca169eb612f5ed5"><code>3dd33f8</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4249">#4249</a>
from github/mbg/upload-improvements-for-4223</li>
<li><a
href="https://github.com/github/codeql-action/commit/b96e3390db93dc46c2c3753a94b87c0d734b0b61"><code>b96e339</code></a>
Change comment for <code>getConfig</code> call in
<code>upload-sarif</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/7fa45180db8d657b23ded3636b5d8583aec6ddfe"><code>7fa4518</code></a>
Use <code>shouldSkipSarifUpload</code> in
<code>analyze-action.ts</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/a69c7cb332d56f616fcadef002884523c71e8d1c"><code>a69c7cb</code></a>
Document that setting the env vars to <code>false</code> takes
precedence</li>
<li><a
href="https://github.com/github/codeql-action/commit/74ddcd9f65683791ab07eccd074b4ba145d89ea6"><code>74ddcd9</code></a>
Fix typo in comment</li>
<li>Additional commits viewable in <a
href="https://github.com/github/codeql-action/compare/6f2ac81f5cd81fe351a197ba0b00d91d03cd2aee...9b3254085494b55a0f7c4c2b3d2d52cc712ce370">compare
view</a></li>
</ul>
</details>
<br />

Updates `github/codeql-action/upload-sarif` from 4.39.0 to 4.39.1
<details>
<summary>Release notes</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/releases">github/codeql-action/upload-sarif's
releases</a>.</em></p>
<blockquote>
<h2>v4.39.1</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
</blockquote>
</details>
<details>
<summary>Changelog</summary>
<p><em>Sourced from <a
href="https://github.com/github/codeql-action/blob/main/CHANGELOG.md">github/codeql-action/upload-sarif's
changelog</a>.</em></p>
<blockquote>
<h1>CodeQL Action Changelog</h1>
<p>See the <a
href="https://github.com/github/codeql-action/releases">releases
page</a> for the relevant changes to the CodeQL CLI and language
packs.</p>
<h2>[UNRELEASED]</h2>
<p>No user facing changes.</p>
<h2>4.39.1 - 21 Oct 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.3">2.27.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4256">#4256</a></li>
</ul>
<h2>4.39.0 - 15 Oct 2026</h2>
<ul>
<li><em>Breaking change</em>: Bump the minimum required CodeQL bundle
version to 2.20.7. <a
href="https://redirect.github.com/github/codeql-action/pull/4205">#4205</a></li>
<li>The <code>codeql-action/analyze</code> step now validates that a
correct argument for the <code>checkout_path</code> input has been
provided. The <code>checkout_path</code> input must be set to the path
where the repository that is being analyzed is checked out at on the
runner, if that path is something other than the workspace root. If the
path does not point to a repository checkout or is different from the
path that was used by <code>codeql-action/init</code>, then the CodeQL
Action now produces a warning. <a
href="https://redirect.github.com/github/codeql-action/pull/4148">#4148</a></li>
<li>Resolved an issue with third-party caching implementations that
prevented caches from being restored correctly. <a
href="https://redirect.github.com/github/codeql-action/pull/4206">#4206</a></li>
<li>The <code>codeql-action/start-proxy</code> step that is used in Code
Scanning Default Setup now finds CodeQL releases using the same logic as
<code>codeql-action/init</code>. This primarily benefits customers who
are using GitHub instances other than <code>github.com</code> where the
<code>codeql-action/start-proxy</code> step may previously have been
unable to locate recent releases and ended up using outdated versions of
the private registry authentication proxy as a result. <a
href="https://redirect.github.com/github/codeql-action/pull/4198">#4198</a></li>
</ul>
<h2>4.38.3 - 08 Oct 2026</h2>
<ul>
<li><em>Upcoming breaking change</em>: CodeQL version 2.21.2 and earlier
were discontinued on 24 September 2026 alongside GitHub Enterprise
Server 3.17, and will be unsupported by the next minor release of the
CodeQL Action. Added a deprecation warning for customers using these
versions of CodeQL. <a
href="https://redirect.github.com/github/codeql-action/pull/4188">#4188</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.2">2.27.2</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4203">#4203</a></li>
<li>Fixed a bug where the decision of whether to use a per-language
bundle did not account for custom configurations that reference queries
outside of compiled CodeQL packs. This issue was caught during internal
testing and did not affect any customer repositories. We will resume the
roll out of per-language bundles in the coming weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4184">#4184</a></li>
</ul>
<h2>4.38.2 - 24 Sept 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.1">2.27.1</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4160">#4160</a></li>
</ul>
<h2>4.38.1 - 18 Sept 2026</h2>
<ul>
<li>The CodeQL Action now has experimental support for CodeQL releases
for which per-language bundles are available. Per-language bundles
support analysis for a single language and are therefore smaller than
the combined bundles that allow analysis for all supported languages. As
a result, per-language bundles take up less space on disk and are faster
to download. We expect to roll this change out to everyone in the coming
weeks. <a
href="https://redirect.github.com/github/codeql-action/pull/4146">#4146</a></li>
</ul>
<h2>4.38.0 - 09 Sept 2026</h2>
<ul>
<li>On GitHub-hosted runners, the CodeQL Action now deletes unused
CodeQL bundles from the toolcache before downloading a different bundle,
which frees up disk space for the analysis. We expect to roll this
change out to everyone in September. <a
href="https://redirect.github.com/github/codeql-action/pull/4124">#4124</a></li>
<li>The CodeQL Action now supports CodeQL releases that are compatible
with Linux Arm64 and downloads the native <code>linux-arm64</code>
CodeQL bundle when available. <a
href="https://redirect.github.com/github/codeql-action/pull/4072">#4072</a></li>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.27.0">2.27.0</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4129">#4129</a></li>
</ul>
<h2>4.37.9 - 26 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.4">2.26.4</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4106">#4106</a></li>
</ul>
<h2>4.37.8 - 21 Aug 2026</h2>
<p>No user facing changes.</p>
<h2>4.37.7 - 13 Aug 2026</h2>
<ul>
<li>Update default CodeQL bundle version to <a
href="https://github.com/github/codeql-action/releases/tag/codeql-bundle-v2.26.3">2.26.3</a>.
<a
href="https://redirect.github.com/github/codeql-action/pull/4085">#4085</a></li>
</ul>
<!-- raw HTML omitted -->
</blockquote>
<p>... (truncated)</p>
</details>
<details>
<summary>Commits</summary>
<ul>
<li><a
href="https://github.com/github/codeql-action/commit/9b3254085494b55a0f7c4c2b3d2d52cc712ce370"><code>9b32540</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4257">#4257</a>
from github/update-v4.39.1-c5a2f4b0f</li>
<li><a
href="https://github.com/github/codeql-action/commit/b5e1ed9574dcfa81c88c318140f3b3e5c199bfb3"><code>b5e1ed9</code></a>
Trigger workflows</li>
<li><a
href="https://github.com/github/codeql-action/commit/20f5ec39109073afe1789b098456b2be0164f4ee"><code>20f5ec3</code></a>
Update changelog for v4.39.1</li>
<li><a
href="https://github.com/github/codeql-action/commit/c5a2f4b0fe28ca06eaaeb86fb05a5f612ae293f9"><code>c5a2f4b</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4245">#4245</a>
from github/henrymercer/graduate-overlay-trap-caching</li>
<li><a
href="https://github.com/github/codeql-action/commit/61a5a80dd98ad1b9679010141a46cace51065761"><code>61a5a80</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4256">#4256</a>
from github/update-bundle/codeql-bundle-v2.27.3</li>
<li><a
href="https://github.com/github/codeql-action/commit/3dd33f8b69588bd9591684b2dca169eb612f5ed5"><code>3dd33f8</code></a>
Merge pull request <a
href="https://redirect.github.com/github/codeql-action/issues/4249">#4249</a>
from github/mbg/upload-improvements-for-4223</li>
<li><a
href="https://github.com/github/codeql-action/commit/b96e3390db93dc46c2c3753a94b87c0d734b0b61"><code>b96e339</code></a>
Change comment for <code>getConfig</code> call in
<code>upload-sarif</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/7fa45180db8d657b23ded3636b5d8583aec6ddfe"><code>7fa4518</code></a>
Use <code>shouldSkipSarifUpload</code> in
<code>analyze-action.ts</code></li>
<li><a
href="https://github.com/github/codeql-action/commit/a69c7cb332d56f616fcadef002884523c71e8d1c"><code>a69c7cb</code></a>
Document that setting the env vars to <code>false</code> takes
precedence</li>
<li><a
href="https://github.com/github/codeql-action/commit/74ddcd9f65683791ab07eccd074b4ba145d89ea6"><code>74ddcd9</code></a>
Fix typo in comment</li>
<li>Additional commits viewable in <a
href="https://github.com/github/codeql-action/compare/6f2ac81f5cd81fe351a197ba0b00d91d03cd2aee...9b3254085494b55a0f7c4c2b3d2d52cc712ce370">compare
view</a></li>
</ul>
</details>
<br />


Dependabot will resolve any conflicts with this PR as long as you don't
alter it yourself. You can also trigger a rebase manually by commenting
`@dependabot rebase`.

[//]: # (dependabot-automerge-start)
[//]: # (dependabot-automerge-end)

---

<details>
<summary>Dependabot commands and options</summary>
<br />

You can trigger Dependabot actions by commenting on this PR:
- `@dependabot rebase` will rebase this PR
- `@dependabot recreate` will recreate this PR, overwriting any edits
that have been made to it
- `@dependabot show <dependency name> ignore conditions` will show all
of the ignore conditions of the specified dependency
- `@dependabot ignore <dependency name> major version` will close this
group update PR and stop Dependabot creating any more for the specific
dependency's major version (unless you unignore this specific
dependency's major version or upgrade to it yourself)
- `@dependabot ignore <dependency name> minor version` will close this
group update PR and stop Dependabot creating any more for the specific
dependency's minor version (unless you unignore this specific
dependency's minor version or upgrade to it yourself)
- `@dependabot ignore <dependency name>` will close this group update PR
and stop Dependabot creating any more for the specific dependency
(unless you unignore this specific dependency or upgrade to it yourself)
- `@dependabot unignore <dependency name>` will remove all of the ignore
conditions of the specified dependency
- `@dependabot unignore <dependency name> <ignore condition>` will
remove the ignore condition of the specified dependency and ignore
conditions


</details>

Signed-off-by: dependabot[bot] <support@github.com>
Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
Bumps [actions/setup-node](https://github.com/actions/setup-node) from 6.5.0 to 7.1.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/actions/setup-node/releases">actions/setup-node's releases</a>.</em></p> <blockquote> <h2>v7.1.0</h2> <h2>What's Changed</h2> <h3>Enhancements:</h3> <ul> <li>Add support for mise.toml file by <a href="https://github.com/gperdomor"><code>@gperdomor</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1421">actions/setup-node#1421</a></li> <li>Support absolute paths in node-version-file by <a href="https://github.com/v-mahabaleshwars"><code>@v-mahabaleshwars</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1633">actions/setup-node#1633</a></li> </ul> <h3>Bug fixes:</h3> <ul> <li>Add Node version validation and manifest fetch retry by <a href="https://github.com/v-jitenderpalsingh"><code>@v-jitenderpalsingh</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1580">actions/setup-node#1580</a></li> </ul> <h3>Documentation updates:</h3> <ul> <li>README.md: bump actions/checkout to latest version 7 by <a href="https://github.com/deining"><code>@deining</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1578">actions/setup-node#1578</a></li> <li>docs: add V7 ESM migration and NODE_AUTH_TOKEN behavior change by <a href="https://github.com/v-gowridurgad"><code>@v-gowridurgad</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1593">actions/setup-node#1593</a></li> <li>Fixed cache recommendation syntax by <a href="https://github.com/SubJunk"><code>@SubJunk</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1603">actions/setup-node#1603</a></li> </ul> <h3>Dependency updates:</h3> <ul> <li>Update workflow pins and migrate Node matrices to modern versions by <a href="https://github.com/v-HarithaVattikuti"><code>@v-HarithaVattikuti</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1583">actions/setup-node#1583</a></li> <li>Upgrade <code>@actions/cache</code> to 6.2.0 by <a href="https://github.com/philip-gai"><code>@philip-gai</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1584">actions/setup-node#1584</a></li> <li>Pin <code>@types/node</code> to v24 by <a href="https://github.com/v-priyagupta108"><code>@v-priyagupta108</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1585">actions/setup-node#1585</a></li> <li>Override brace-expansion to 5.0.8 by <a href="https://github.com/v-priyagupta108"><code>@v-priyagupta108</code></a> with <a href="https://github.com/Copilot"><code>@Copilot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1599">actions/setup-node#1599</a></li> <li>Upgrade actions/checkout from 7.0.0 to 7.0.1 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1598">actions/setup-node#1598</a></li> <li>Upgrade prettier from 3.8.4 to 3.9.6 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1590">actions/setup-node#1590</a></li> <li>Upgrade <code>@vercel/ncc</code> from 0.44.0 to 0.45.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1610">actions/setup-node#1610</a></li> <li>Upgrade pnpm/action-setup from 6.0.9 to 6.0.10 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1602">actions/setup-node#1602</a></li> <li>Upgrade baseline-browser-mapping from 2.10.38 to 2.11.22 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1629">actions/setup-node#1629</a></li> <li>Upgrade <code>@types/semver</code> from 7.7.1 to 7.8.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1616">actions/setup-node#1616</a></li> <li>Upgrade <code>@typescript-eslint/parser</code> from 8.62.0 to 8.70.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1615">actions/setup-node#1615</a></li> <li>Upgrade pnpm/action-setup from 6.0.10 to 6.1.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1631">actions/setup-node#1631</a></li> <li>Upgrade jest-each from 30.4.1 to 30.5.2 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1636">actions/setup-node#1636</a></li> <li>Upgrade eslint-plugin-n from 18.1.0 to 18.3.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1638">actions/setup-node#1638</a></li> <li>Update dependencies and add license files by <a href="https://github.com/v-HarithaVattikuti"><code>@v-HarithaVattikuti</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1642">actions/setup-node#1642</a></li> <li>Upgrade eslint from 10.5.0 to 10.11.0 and package.json from 7.0.0 to 7.1.0 by <a href="https://github.com/dependabot"><code>@dependabot</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1635">actions/setup-node#1635</a></li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/v-jitenderpalsingh"><code>@v-jitenderpalsingh</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-node/pull/1580">actions/setup-node#1580</a></li> <li><a href="https://github.com/philip-gai"><code>@philip-gai</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-node/pull/1584">actions/setup-node#1584</a></li> <li><a href="https://github.com/gperdomor"><code>@gperdomor</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-node/pull/1421">actions/setup-node#1421</a></li> <li><a href="https://github.com/SubJunk"><code>@SubJunk</code></a> made their first contribution in <a href="https://redirect.github.com/actions/setup-node/pull/1603">actions/setup-node#1603</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/actions/setup-node/compare/v7.0.0...v7.1.0">https://github.com/actions/setup-node/compare/v7.0.0...v7.1.0</a></p> <h2>v7.0.0</h2> <h2>What's Changed</h2> <h3>Enhancements:</h3> <ul> <li>Add cache-primary-key and cache-matched-key as outputs by <a href="https://github.com/gowridurgad"><code>@gowridurgad</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1577">actions/setup-node#1577</a></li> <li>Migrate to ESM and upgrade dependencies by <a href="https://github.com/gowridurgad"><code>@gowridurgad</code></a> in <a href="https://redirect.github.com/actions/setup-node/pull/1574">actions/setup-node#1574</a></li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/actions/setup-node/commit/949feb2413d6458794dcd2491c4babbbce0c15c1"><code>949feb2</code></a> Bump eslint from 10.5.0 to 10.11.0 and package.json from 7.0.0 to 7.1.0 (<a href="https://redirect.github.com/actions/setup-node/issues/1635">#1635</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/7207c4f1189c7ee83ddf20c7c68bd1af6fdd751c"><code>7207c4f</code></a> chore: update dependencies and add license files (<a href="https://redirect.github.com/actions/setup-node/issues/1642">#1642</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/54337e0d02de9202d0948aaff36ad556375497b9"><code>54337e0</code></a> Bump eslint-plugin-n from 18.1.0 to 18.3.0 (<a href="https://redirect.github.com/actions/setup-node/issues/1638">#1638</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/fb54fa8c14c63410cc752f0ae3b7b3ca6af161fc"><code>fb54fa8</code></a> Bump jest-each from 30.4.1 to 30.5.2 (<a href="https://redirect.github.com/actions/setup-node/issues/1636">#1636</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/7f84f1d52d0c56afb45c62fee31a93b843cea4d6"><code>7f84f1d</code></a> Bump pnpm/action-setup from 6.0.10 to 6.1.0 (<a href="https://redirect.github.com/actions/setup-node/issues/1631">#1631</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/0c54c7b07420dcba69a7d832587f55ebdf771c9e"><code>0c54c7b</code></a> Bump <code>@typescript-eslint/parser</code> from 8.62.0 to 8.70.0 (<a href="https://redirect.github.com/actions/setup-node/issues/1615">#1615</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/a8294190049a9c296f01b9a432aff41dd83d8284"><code>a829419</code></a> Bump <code>@types/semver</code> from 7.7.1 to 7.8.0 (<a href="https://redirect.github.com/actions/setup-node/issues/1616">#1616</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/680d1e489b82f1243de15bc7665c0007e3c9a860"><code>680d1e4</code></a> Support absolute paths in node-version-file (<a href="https://redirect.github.com/actions/setup-node/issues/1633">#1633</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/db0fb3a98ed314b69026b6e8c9be26a7e2fe65a8"><code>db0fb3a</code></a> Bump baseline-browser-mapping from 2.10.38 to 2.11.22 (<a href="https://redirect.github.com/actions/setup-node/issues/1629">#1629</a>)</li> <li><a href="https://github.com/actions/setup-node/commit/94196ee1d15439c1b6651cd87ef14e88ec435966"><code>94196ee</code></a> Bump pnpm/action-setup from 6.0.9 to 6.0.10 (<a href="https://redirect.github.com/actions/setup-node/issues/1602">#1602</a>)</li> <li>Additional commits viewable in <a href="https://github.com/actions/setup-node/compare/v6.5.0...949feb2413d6458794dcd2491c4babbbce0c15c1">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
### Description
<!-- Describe your changes. -->

1. Stage an explicit allowlist for the provider and core test suites and
run each executable in its own pipeline step.

2. Update shader key validation to account for configuration
differences.

3. Disable CodeQL to speed up builds.

### Motivation and Context
<!-- - Why is this change required? What problem does it solve?
- If it fixes an open issue, please link to the issue here. -->

Fix pipeline failures. Rationale for the numbered changes above:

1. There are binskim issues with the unrelated
onnxruntime_telemetry_shutdown_test_library test DLL. We don't need to
run onnxruntime_telemetry_shutdown_test for this check so we can avoid
staging its binaries. Fixing the binskim issues (from disabling
dependency warnings) would be good but it is outside of the scope of
this pipeline check.

2. There was a new shader key validation failure caused by a recently
added unit test that uses a non-default WebGPU context with a different
configuration.

---------

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Bumps [qs](https://github.com/ljharb/qs) and [body-parser](https://github.com/expressjs/body-parser). These dependencies needed to be updated together. Updates `qs` from 6.15.2 to 6.16.2 <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/ljharb/qs/blob/main/CHANGELOG.md">qs's changelog</a>.</em></p> <blockquote> <h2><strong>6.16.2</strong></h2> <ul> <li>[Fix] <code>stringify</code>: encode keys when <code>allowEmptyArrays</code> is set (<a href="https://redirect.github.com/ljharb/qs/issues/561">#561</a>)</li> <li>[meta] use double quotes for better OS support</li> <li>[Dev Deps] update <code>evalmd</code>, <code>npmignore</code></li> <li>[Tests] <code>stringify</code>: pin <code>allowEmptyArrays</code> output for keys that need no encoding</li> </ul> <h2><strong>6.16.1</strong></h2> <ul> <li>[Fix] <code>parse</code>: do not mutate an object input</li> <li>[Fix] <code>stringify</code>: stop re-encoding structural separator dots when <code>encodeDotInKeys</code> is set (<a href="https://redirect.github.com/ljharb/qs/issues/564">#564</a>)</li> <li>[Fix] <code>stringify</code>: <code>arrayFormat: 'comma'</code>: pass the full encoder arguments with <code>encodeValuesOnly</code></li> <li>[Fix] <code>utils</code>: encode <code>+</code> as <code>%2B</code> in iso-8859-1 mode so values round-trip (<a href="https://redirect.github.com/ljharb/qs/issues/565">#565</a>)</li> <li>[Fix] parse: only convert top-level dots to brackets when allowDots is on (<a href="https://redirect.github.com/ljharb/qs/issues/621">#621</a>)</li> <li>[Fix] <code>stringify</code>: ignore inherited array format names (<a href="https://redirect.github.com/ljharb/qs/issues/622">#622</a>)</li> <li>[Fix] <code>stringify</code>: <code>arrayFormat: 'comma'</code>: do not throw on elements with no callable <code>toString</code></li> <li>[Fix] <code>utils</code>: <code>merge</code>: seed an overflow container's index from its own keys, not just the source</li> <li>[Fix] <code>utils</code>: <code>merge</code>: keep a <code>strictMerge</code> conflict container's index and <code>arrayLimit</code> correct</li> <li>[Fix] <code>parse</code>: only treat <code>[]</code> as array syntax when it ends the key</li> <li>[Perf] <code>decode</code>: skip decoders when there is no percent sign (<a href="https://redirect.github.com/ljharb/qs/issues/583">#583</a>)</li> <li>[Robustness] <code>utils</code>: <code>merge</code>: apply <code>arrayLimit</code> to the two-element array built for colliding values</li> <li>[Robustness] <code>parse</code>: bound the nesting added by repeated <code>strictMerge</code> conflicts (credit <a href="https://github.com/Yeaseen"><code>@Yeaseen</code></a>)</li> <li>[Docs] document that <code>qs</code> and flat parsers disagree about parameter names</li> <li>[Docs] clarify that <code>throwOnLimitExceeded</code> limits each array, not the total number of values</li> <li>[Docs] clarify 6.14.1/6.15.2 parse bracket behavior change (<a href="https://redirect.github.com/ljharb/qs/issues/567">#567</a>, <a href="https://redirect.github.com/ljharb/qs/issues/568">#568</a>)</li> <li>[meta] fix changelog indents</li> <li>[actions] set least-privilege <code>cache-mode</code></li> <li>[Tests] <code>utils</code>: <code>decode</code>: add missing cases</li> <li>[Tests] <code>parse</code>: characterize the <code>]=</code> split when an <code>=</code> precedes any bracket group (<a href="https://redirect.github.com/ljharb/qs/issues/620">#620</a>)</li> <li>[Tests] <code>parse</code>: <code>allowDots</code>: cover stray close brackets before a dot</li> <li>[Dev Deps] update <code>@ljharb/eslint-config</code>, <code>eslint</code>, <code>tape</code></li> </ul> <h2><strong>6.16.0</strong></h2> <ul> <li>[New] <code>stringify</code>: add a <code>depth</code> option to bound recursion depth (default <code>Infinity</code>)</li> <li>[Fix] stringify: serialize Date values when a filter is provided</li> <li>[Fix] <code>parse</code>: enforce <code>arrayLimit</code> on comma groups under <code>[]=</code> when <code>throwOnLimitExceeded</code> is set</li> <li>[Fix] <code>parse</code>: flatten a collection appended to an overflowed array (<a href="https://redirect.github.com/ljharb/qs/issues/571">#571</a>)</li> <li>[Fix] <code>utils</code>: <code>isBuffer</code>: do not invoke a non-callable <code>constructor.isBuffer</code></li> <li>[Fix] <code>stringify</code>: do not let <code>allowEmptyArrays</code> skip cycle detection (or drop own keys) on an empty array with own properties</li> <li>[Fix] <code>stringify</code>: encode dots in a top-level key with a primitive value when encodeDotInKeys is set (<a href="https://redirect.github.com/ljharb/qs/issues/562">#562</a>)</li> <li>[Docs] threat model: clarify <code>stringify</code> deep-nesting DoS is caller-bounded</li> <li>[Docs] clarify <code>arrayLimit</code> is a representation threshold, not an element-count cap</li> <li>[Tests] <code>parse</code>: remove a test that pinned <code>[]=</code> comma groups escaping <code>arrayLimit</code></li> <li>[Tests] <code>stringify</code>: pin current <code>encodeDotInKeys</code> separator-dot behavior</li> <li>[Dev Deps] update <code>@ljharb/eslint-config</code>, <code>eslint</code></li> <li>[Dev Deps] update <code>eslint</code>, <code>evalmd</code></li> </ul> <h2><strong>6.15.4</strong></h2> <ul> <li>[Fix] <code>stringify</code>: encode keys when <code>allowEmptyArrays</code> is set (<a href="https://redirect.github.com/ljharb/qs/issues/561">#561</a>)</li> <li>[meta] use double quotes for better OS support</li> <li>[Dev Deps] update <code>@ljharb/eslint-config</code>, <code>evalmd</code>, <code>npmignore</code>, <code>tape</code></li> <li>[Tests] <code>stringify</code>: pin <code>allowEmptyArrays</code> output for keys that need no encoding</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/ljharb/qs/commit/136912a619c2d81c090ca196ea02b6c193580d1d"><code>136912a</code></a> v6.16.2</li> <li><a href="https://github.com/ljharb/qs/commit/6ed1c73b103440d51a0b573d6f629a457ea625ce"><code>6ed1c73</code></a> [Dev Deps] update <code>evalmd</code>, <code>npmignore</code></li> <li><a href="https://github.com/ljharb/qs/commit/a09bc29e5718f661ea66d39feb8f5b1fb1c4fa18"><code>a09bc29</code></a> [meta] use double quotes for better OS support</li> <li><a href="https://github.com/ljharb/qs/commit/5d3b1b9ec6afd0cfc760c8e12862873789a32fc8"><code>5d3b1b9</code></a> [Fix] <code>stringify</code>: encode keys when <code>allowEmptyArrays</code> is set</li> <li><a href="https://github.com/ljharb/qs/commit/f13ec6c2eb9d4fb59508dfa29e73952c4ffc68a3"><code>f13ec6c</code></a> [Tests] <code>stringify</code>: pin <code>allowEmptyArrays</code> output for keys that need no enco...</li> <li><a href="https://github.com/ljharb/qs/commit/2471b66ae696a8a10915c01453ae2c0f139a5adc"><code>2471b66</code></a> v6.16.1</li> <li><a href="https://github.com/ljharb/qs/commit/51f736e94b079b8479fa8f668acba84c1e177596"><code>51f736e</code></a> [Docs] document that <code>qs</code> and flat parsers disagree about parameter names</li> <li><a href="https://github.com/ljharb/qs/commit/40239f7564e99ab92eb9125defaaf4779a26b03a"><code>40239f7</code></a> [Dev Deps] update <code>tape</code></li> <li><a href="https://github.com/ljharb/qs/commit/d219359f5bedc42815190b2448160fae06b7817c"><code>d219359</code></a> [Fix] <code>parse</code>: do not mutate an object input</li> <li><a href="https://github.com/ljharb/qs/commit/98157dc1b770240ed4fb91da0faa3fb404b80474"><code>98157dc</code></a> [Fix] <code>stringify</code>: stop re-encoding structural separator dots when `encodeDot...</li> <li>Additional commits viewable in <a href="https://github.com/ljharb/qs/compare/v6.15.2...v6.16.2">compare view</a></li> </ul> </details> <br /> Updates `body-parser` from 1.20.5 to 1.20.9 <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/expressjs/body-parser/releases">body-parser's releases</a>.</em></p> <blockquote> <h2>1.20.9</h2> <h2>Important: Security</h2> <ul> <li>Security fix for <a href="https://www.cve.org/CVERecord?id=CVE-2026-111181">CVE-2026-111181</a> (<a href="https://github.com/expressjs/body-parser/security/advisories/GHSA-27r3-jxmh-p828">GHSA-27r3-jxmh-p828</a>)</li> </ul> <h2>What's Changed</h2> <ul> <li>Release: 1.20.9 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/779">expressjs/body-parser#779</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/body-parser/compare/1.20.8...1.20.9">https://github.com/expressjs/body-parser/compare/1.20.8...1.20.9</a></p> <h2>1.20.8</h2> <h2>Important</h2> <p><strong>Same code base as <a href="https://github.com/expressjs/body-parser/releases/tag/1.20.7">1.20.7</a>. This was created to test the new release process.</strong></p> <h2>What's Changed</h2> <ul> <li>ci: backport npm-publish workflow from master by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/769">expressjs/body-parser#769</a></li> <li>1.20.8 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/770">expressjs/body-parser#770</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/body-parser/compare/1.20.7...1.20.8">https://github.com/expressjs/body-parser/compare/1.20.7...1.20.8</a></p> <h2>1.20.7</h2> <h2>What's Changed</h2> <ul> <li>docs: include security fix in 1.20.6 changes by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/747">expressjs/body-parser#747</a></li> <li>deps: qs@~6.16.0 by <a href="https://github.com/krzysdz"><code>@krzysdz</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/761">expressjs/body-parser#761</a></li> <li>1.20.7 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/767">expressjs/body-parser#767</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/body-parser/compare/1.20.6...1.20.7">https://github.com/expressjs/body-parser/compare/1.20.6...1.20.7</a></p> <h2>1.20.6</h2> <h2>Important: Security</h2> <ul> <li>Security fix for <a href="https://www.cve.org/CVERecord?id=CVE-2025-13466">CVE-2026-12590</a> (<a href="https://github.com/expressjs/body-parser/security/advisories/GHSA-v422-hmwv-36x6">GHSA-v422-hmwv-36x6</a>)</li> </ul> <h2>What's Changed</h2> <ul> <li>fix: improve limit option validation by <a href="https://github.com/Phillip9587"><code>@Phillip9587</code></a> in <a href="https://redirect.github.com/expressjs/body-parser/pull/741">expressjs/body-parser#741</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/body-parser/compare/1.20.5...1.20.6">https://github.com/expressjs/body-parser/compare/1.20.5...1.20.6</a></p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/expressjs/body-parser/blob/1.20.9/HISTORY.md">body-parser's changelog</a>.</em></p> <blockquote> <h1>1.20.9</h1> <ul> <li>Security fix for <a href="https://github.com/expressjs/body-parser/security/advisories/GHSA-27r3-jxmh-p828">GHSA-27r3-jxmh-p828</a> (CVE-2026-111181)</li> </ul> <h1>1.20.8</h1> <ul> <li>Same code base as 1.20.7. This was created to test the new release process.</li> </ul> <h1>1.20.7</h1> <ul> <li>deps: qs@~6.16.0</li> </ul> <h1>1.20.6</h1> <ul> <li>Security fix for <a href="https://github.com/expressjs/body-parser/security/advisories/GHSA-v422-hmwv-36x6">GHSA-v422-hmwv-36x6</a></li> <li>fix: improve <code>limit</code> option validation (<a href="https://redirect.github.com/expressjs/body-parser/issues/698">#698</a>) <ul> <li>Invalid <code>limit</code> values (e.g. unparseable strings or <code>NaN</code>) now throw instead of being silently ignored, which previously disabled size limit enforcement</li> <li><code>null</code> and <code>undefined</code> fall back to the default 100kb limit</li> </ul> </li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/expressjs/body-parser/commit/a64f1404e256b3f0e3ce633e081a7593fe482203"><code>a64f140</code></a> 1.20.9 (<a href="https://redirect.github.com/expressjs/body-parser/issues/779">#779</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/1260c3845f54502a05a87594f09a334786bb34d7"><code>1260c38</code></a> fix: prevent process crash from trailing bytes after a compressed body</li> <li><a href="https://github.com/expressjs/body-parser/commit/b4c2112ff66163da4304188edda5690e90f7c8a7"><code>b4c2112</code></a> docs: fix depth error description (<a href="https://redirect.github.com/expressjs/body-parser/issues/776">#776</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/29ddb9b43385d3b2c16003aeb8934913ec274011"><code>29ddb9b</code></a> docs: improve readability (<a href="https://redirect.github.com/expressjs/body-parser/issues/756">#756</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/ac9667a35e178f2c4465fb0298679cfb46629584"><code>ac9667a</code></a> docs: improve wording (<a href="https://redirect.github.com/expressjs/body-parser/issues/755">#755</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/5c08c2008eac79abddb8abfa5095491d02958d56"><code>5c08c20</code></a> 1.20.8 (<a href="https://redirect.github.com/expressjs/body-parser/issues/770">#770</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/0cea4f42a40996eafac441d0e71084afbe1407d4"><code>0cea4f4</code></a> ci: backport npm-publish workflow from master (<a href="https://redirect.github.com/expressjs/body-parser/issues/769">#769</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/0f0f0d7f96fc7444407aef85a6d1fa363279e654"><code>0f0f0d7</code></a> 1.20.7 (<a href="https://redirect.github.com/expressjs/body-parser/issues/767">#767</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/355eb04ade7c27f57f93a0e90e26ed6f121becc5"><code>355eb04</code></a> deps: qs@~6.16.0 (<a href="https://redirect.github.com/expressjs/body-parser/issues/761">#761</a>)</li> <li><a href="https://github.com/expressjs/body-parser/commit/8be369a5f8b0f4070ebb7a0ae9aca12db9d8f947"><code>8be369a</code></a> docs: include security fix in 1.20.6 changes</li> <li>Additional commits viewable in <a href="https://github.com/expressjs/body-parser/compare/1.20.5...1.20.9">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for body-parser since your current version.</p> </details> <br /> Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) You can disable automated security fix PRs for this repo from the [Security Alerts page](https://github.com/microsoft/onnxruntime/network/alerts). </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>

### Description
<!-- Describe your changes. -->

Introduce an experimental, explicitly opt-in C++ graph pattern rewriter
in `onnxruntime::rewrite`, with documentation and component/integration
tests. This is infrastructure for authoring rewrites, not a production
fusion rollout; it is not registered among ORT's default optimizers.

- Provide independently usable `Pattern::MatchAt` / `VisitMatches` and
`Replacement::Instantiate` APIs, candidate-local `Match` bindings, C++
check-and-bind callbacks, rewrite rules, and a
`GraphTransformer`-compatible engine.
- Add a text DSL for connected DAG patterns and replacements, positional
multi-output bindings, constants and attributes, optional tensor slots,
type/shape constraints, immutable tensor constraints, and typed constant
readers.
- Support reusable named pattern libraries, hygienic nested calls,
interfaces, aliases and bounded source-order alternatives. Scoped
binding views expose the selected alternative; handwritten C++ views
illustrate usage without adding a code generator.
- Support optional attribute captures such as `perm : ints | None`,
distinguishing captured absence from unknown names, with nullable lookup
and replacement omission followed by schema default/required-attribute
validation.
- Preserve graph-output/external-user deletion boundaries,
provider/layer and explicit opset eligibility, candidate binding
isolation, deterministic rule priority, and staging/rollback before
committing a replacement. Replacement errors propagate rather than
silently retrying. Whole engine runs and subsequent `Graph::Resolve` are
not transactional.
- Document component contracts, borrowed graph lifetimes, Resolve
boundaries, bounded matching, diagnostics, opt-in integration, and
natural Transpose-composition plus small numerical fusion examples. No
MoE/QMoE lowering or sibling fusion changes are included.

Validation already performed on Windows CPU Release at implementation
commit `e5927feb856711fc0f4c06145a553c1c2675cdf9`; the subsequent head
`319fa38a679b3730ca7487c2269fa388dca58f2b` changes documentation
order/cross-links only:

```powershell
.\.venv\Scripts\python.exe tools\ci_build\build.py --config Release --build_dir C:\ortbuild\rewriter3 --build --parallel 12 --target onnxruntime_test_all --skip_submodule_sync --compile_no_warning_as_error --no_telemetry
```

Result: passed incremental Release build.

From `C:\ortbuild\rewriter3\Release\Release`:

```powershell
.\onnxruntime_test_all.exe --gtest_filter=PatternComponentTests.*:ReplacementComponentTests.*:MatchComponentTests.*:CheckAndBindComponentTests.*:PatternRewriterTests.*
```

Result: 155 tests passed across five suites, including component
contracts, numerical CPU equivalence, composition/alternative retry,
optional attributes, graph boundaries and replacement rollback.

Independent focused review additionally rebuilt the engine and
artifact-only harnesses, passed 100 grouped optional-attribute checks
plus existing component/dimension/positional checks, and compiled both
test translation units in normal and `DISABLE_CONTRIB_OPS`
configurations (four successful compiles). The reviewer also reran the
owner-built 155-test executable. These are local results, not upstream
CI results. No clean full runtime rebuild, disabled-contrib runtime
execution, or GPU validation was performed. Documentation checks
preserve all code examples and verify local anchors, fenced blocks,
heading order and `git diff --check`.

### Motivation and Context
<!-- - Why is this change required? What problem does it solve?
- If it fixes an open issue, please link to the issue here. -->

Graph rewrites combine recurring structural matching and graph-edit
safety logic with rule-specific semantic and kernel-support checks. This
separates those responsibilities: patterns describe structure, C++
check-and-bind functions establish applicability and prepare values,
replacements describe construction, and the engine handles ordered
application.

Standalone matching and fragment construction make each component
independently testable. Reusable pattern composition avoids duplicating
common graph forms while preserving local bindings and explicit
alternative selection. Semantic equivalence, arithmetic/dependent
constraints and kernel compatibility remain the rule author's
responsibility in C++; there are no higher-order pattern parameters,
general recursive backtracking, automatic C++ generation, or default
optimizer behavior changes.

This draft is submitted from the existing
`gramalingam:gramalingam-rewriter3` branch for upstream discussion. It
targets upstream `main` (the current default; `master` is no longer an
actual upstream branch) without rebasing the source branch.

---------

Signed-off-by: Ganesan Ramalingam <grama@microsoft.com>
Co-authored-by: Copilot App <223556219+Copilot@users.noreply.github.com>
Copilot-Session: daf231a0-ce61-4a2b-9649-0f31e2296e4f

### Description

- Evaluate `alpha * 0 + beta * C` when Gemm's reduction dimension is
zero, including bias broadcasting and scaling.
- Use the same zero-K handling for float, double, float16, and the
packed float path so signed-zero behavior is consistent.
- Add CPU regression tests for signed zero and bias scaling, including
float16.

### Motivation and Context

Fixes microsoft#33344. With K=0, `MatMul + Add` produces positive zero for a
negative-zero bias, while the fused Gemm previously returned the
negative-zero bias unchanged. A following Reciprocal then changes from
`+Inf` to `-Inf`. The early return also omitted the `beta` factor.

Before the fix, both new float regression tests failed on the original
code. After the fix, all 53 `GemmOpTest.*` and `GemmOpTypedTests*` tests
pass on Linux CPU. The changed files pass `lintrunner` and `git diff
--check`. The local GCC 15 build used `--compile_no_warning_as_error`
because of a warning in unchanged `logging.cc`.

AI assistance was used to prepare this patch and its tests.

…crosoft#33568)

Prevent CPU QLinearSoftmax from silently returning incorrect results for
a non-positive input
scale.
- **Decline the QDQ fusion** (`DQ -> Softmax -> Q`): Softmax now
requires a positive constant
input scale via `IsQOrDQScalePositiveConstantScalar` (same policy as
microsoft#21182 for
  MaxPool/ReduceMax/ReduceMin).
- **Guard the kernel**: `Compute` returns an error for `x_scale <= 0`
instead of building an
  inverted lookup table and silently returning zeros.

### Motivation and Context

Fixes microsoft#33438. `QlinearBuildLookupTableUint32` centers its exp table on
the max quantized value
255, which is only the max real logit for a positive scale. With
`x_scale = -1`, `table[0] =
exp(338) = inf`, so `vsum = inf` and the output collapses from
`[0.99609375, 0]` to `[0, 0]`.
The unfused graph is correct; only the fusion corrupts it. Same bug
class as microsoft#21176/microsoft#21182.

…icrosoft#33399)

### Description

Use exact unsigned span/step arithmetic for integer `Range` element
counts in the CPU kernel and the `com.microsoft::Range` shape-inference
path. This avoids losing small differences between large int64 endpoints
when converting them separately to double.

- Preserve empty/backward-range behavior, reject zero delta, and reject
counts larger than INT64_MAX before conversion/allocation.
- Avoid computing the unused value after the final emitted element,
which can overflow even when every output is representable.
- Add CPU-only regression coverage for int64 boundaries,
cross-sign/extreme steps, int32/int64 final increments, contrib
initializer inference, and invalid counts/delta.
- Leave floating-point count behavior and CUDA implementation unchanged.
The CUDA comment is updated so it no longer claims integer parity with
CPU.

### Motivation and Context

Fixes microsoft#33292.

For example, `Range(INT64_MAX - 7, INT64_MAX, 2)` should emit four exact
values; converting both endpoints to double first produces an empty
result. The shared integer helper also handles spans larger than
INT64_MAX and INT64_MIN step magnitudes without signed
subtraction/negation.

### Validation

Linux x86_64, GCC 14.2.0, Release CPU build. Initial submission build
and 46-test run performed against upstream
648f708 plus this patch on October 15,
2026.

- Built `onnxruntime_provider_test` and ran
`--gtest_filter='RangeTest.*:ConstantOfShape.*:EyeLikeOpTest.*'`: **46
passed** (34 Range, 12 neighboring generator tests).
- Before-fix check on upstream 9cdf0f1 with the new regression tests
retained: **30 passed, 4 failed**. Restoring this patch makes all 34
Range tests pass.
- On upstream 122c193 plus this patch, a separately rebuilt executable
with signed-overflow instrumentation on the actual CPU `range.cc`
translation unit passed all **34 Range tests**. Restoring the upstream
CPU translation unit detects signed overflow in the final-increment
regression. This is not whole-program sanitizer coverage.
- Configured clang-format 20.1.8 checks for all five changed files and
`git diff --check` passed.

No local CUDA execution, Windows/macOS testing, full repository test
suite, or performance benchmark was run. Standard ONNX static inference
for extreme cross-sign constant inputs is a separate upstream
limitation; those cases use standard runtime inputs and contrib
initializers here.

### Windows build follow-up (October 16, 2026)

The initial Windows builds reported MSVC C4702 (treated as an error)
because the floating-point calculation remained instantiated after the
integral `if constexpr` branch returned. Commit 45096b2 places that
unchanged calculation in the corresponding `else`, so integral
instantiations discard it.

Rebuilt the affected `range_schema_defs.cc` translation unit and
`onnxruntime_provider_test` on Linux, then reran
`RangeTest.*:ConstantOfShape.*:EyeLikeOpTest.*`: **46 passed**.
Clang-format and `git diff --check` passed. Windows/MSVC confirmation is
pending CI for the new commit, which currently requires maintainer
approval; no local Windows pass is claimed.

### AI assistance

OpenAI coding agents assisted with diagnosis, implementation, regression
tests, code review, and this PR description. The test results above are
from actual local execution; they do not assert independent human
review.


## Description

This change enables CPU EP execution of A16 models that contain
block-quantized weights with authored `MatMulNBits` block sizes above
256.

It addresses two issues:

1. Constant-weight `DequantizeLinear -> MatMul/Gemm` patterns were not
converted to `MatMulNBits` when the operation was enclosed by 16-bit
activation Q/DQ boundaries.
2. CPU `MatMulNBits` rejected all block sizes above 256, including
models authored with `block_size=1024`.

## Changes

### Fuse weight DQ inside 16-bit activation boundaries

Add a CPU-only `DQMatMulToMatMulNBits_A16` selector that can convert the
constant weight path while preserving surrounding INT16/UINT16
activation boundaries.

The selector:

- Identifies activation, weight, and optional bias DQ nodes by the
target input they feed.
- Removes only the constant weight DQ and the MatMul/Gemm target.
- Leaves activation DQ, optional bias DQ, and output Q nodes connected
to the replacement `MatMulNBits`.
- Supports input-only, output-only, and combined A16 boundaries.
- Preserves the existing A8 fusion behavior.
- Rejects unsupported cases such as:
  - INT8/UINT8 activation boundaries in the A16 rule
  - non-CPU targets
  - non-constant or shared weight DQ
  - unsupported Gemm attributes
  - output fan-out to unsupported consumers

### Execute large logical blocks as 256-element sub-blocks

Allow power-of-two `MatMulNBits` block sizes greater than 256 for
supported 4-bit and 8-bit CPU paths.

The authored block layout remains the logical format used to validate
weights, scales, and zero points. For execution, each logical block is
represented as 256-element sub-blocks:

- Scales and zero points are repeated for each execution sub-block.
- Bit-packed zero points are decoded, repeated, and repacked.
- Floating-point zero points are repeated as values.
- Constant quantization parameters are converted once during kernel
creation.
- Runtime scales and zero points are converted per invocation.
- Weight rows are re-strided only when the logical and execution layouts
differ.
- Prepacking, workspace sizing, MLAS capability checks, and compute use
the execution block size.

The following remain explicitly unsupported for block sizes above 256:

- 2-bit weights
- `g_idx`

## Motivation

The supplied encoder contains:

- 48 authored `MatMulNBits` nodes with `block_size=1024`
- 40 authored `MatMulNBits` nodes with `block_size=256`
- 49 constant-weight DQ-to-MatMul/Gemm patterns inside UINT16 activation
boundaries

Stock CPU EP fails during session initialization on the first block-1024
node:

```text
Only block sizes 16, 32, 64, 128, and 256 are supported
for MatMulNBits op, got: 1024

---------

Co-authored-by: Jovan Bubonja <jovanbubonja@microsoft.com>
Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>

### Description
- Accumulate Concat axis dimensions in `int64_t` and reject overflow
before output allocation.
- Validate that every input shape contains the requested concat axis
before reading it.
- Add a CPU regression test with empty symbolic inputs carrying large
axis dimensions.

Tests were not run, per request.

### Motivation and Context
Unchecked `size_t` accumulation could wrap the output axis dimension
when empty inputs carried very large dimensions. This could allocate an
undersized output before copying a non-empty input into it.

---------

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Co-authored-by: Copilot Autofix powered by AI <175728472+Copilot@users.noreply.github.com>

…CropAndResize, Einsum, and AffineGrid kernels (microsoft#33517)

## Summary

When input tensor shapes are dynamic or omitted from `ValueInfoProto` at
model load time, ONNX schema shape inference does not reject rank
mismatches before kernel execution. This PR adds runtime rank checks
(and reorders shape validation before dimension indexing) across six CPU
and contrib operator paths so invalid runtime inputs return a clean
`INVALID_ARGUMENT` / `FAIL` `Status` instead of triggering `gsl::span`
contract-violation `std::terminate()` aborts (or reading past empty
buffers when trailing dimensions are zero):

1. **`ConvAttributes::ValidateInputShape`
(`onnxruntime/core/providers/cpu/nn/conv_attributes.h`)**:
- Checks `input_shape.NumDimensions() >= 3` (minimum rank for 1D
convolution `[N, C, D1]`) after verifying `input_shape.NumDimensions()
== weight_shape.NumDimensions()` and before indexing `weight_shape[0]`,
`input_shape[1]`, and `weight_shape[1]`. Previously, when both `X` and
`W` had rank 0 or rank 1 at runtime (e.g., `X={3}, W={3}, group=3`),
`input_shape.NumDimensions() != weight_shape.NumDimensions()` passed and
`input_shape[1]` / `weight_shape[1]` indexed past the 1-element
`gsl::span`; when both had rank 2 (e.g., `X={1, 1}, W={1, 1}`),
`ValidateInputShape` succeeded with zero spatial dimensions
(`kernel_rank == 0`).

2. **`ConvInteger::Compute`
(`onnxruntime/core/providers/cpu/quantization/conv_integer.cc`)**:
- Moves `ORT_RETURN_IF_ERROR(conv_attrs_.ValidateInputShape(X, W));`
before indexing `X->Shape()[0]`, `X->Shape()[1]`, and `W->Shape()[0]`.
Previously, rank-0 or rank-1 `X` or rank-0 `W` indexed `Shape()[0..1]`
out of bounds before `ValidateInputShape` was reached.

3. **`QLinearConv<ActType>::Compute`
(`onnxruntime/core/providers/cpu/quantization/qlinearconv.cc`)**:
- Moves `ORT_RETURN_IF_ERROR(conv_attrs_.ValidateInputShape(X->Shape(),
W_shape, channels_last_));` before indexing `X->Shape()[0]` and
`W_shape[0]`.

4. **`contrib::CropAndResize<T>::Compute`
(`onnxruntime/contrib_ops/cpu/crop_and_resize.cc`)**:
- Checks `x_dims.NumDimensions() == 4`, `rois_dims.NumDimensions() ==
2`, and `batch_indices_dims.NumDimensions() == 1` before indexing
`x_dims[1]`, `batch_indices_dims[0]`, and `rois_dims[1]` (which
previously ran before `CheckROIAlignValidInput`).
- In addition to preventing low-rank `gsl::span` aborts, enforcing exact
ranks before indexing ensures that `Shape().Size()` equals the product
of the validated dimensions (`x_dims[0..3]`, `rois_dims[0..1]`, and
`batch_indices_dims[0]`), keeping `rois_data`, `batch_indices_data`, and
`X_data` reads in range even when dynamic runtime inputs have a trailing
zero dimension (such as `rois` with shape `{1, 4, 0}` or `batch_indices`
with shape `{1, 0}`).

5. **`EinsumComputePreprocessor::ProcessSubscripts`
(`onnxruntime/core/providers/cpu/math/einsum_utils/einsum_compute_preprocessor.h`)**:
- Moves the excess subscript-label check (`if (dim_counter >= rank)`)
ahead of `auto dim_value = dims[dim_counter];`. Previously, `if
(++dim_counter > rank)` ran at the end of the character loop body after
`dims[dim_counter]` had already been indexed out of bounds.

6. **`AffineGrid<T>::Compute`
(`onnxruntime/core/providers/cpu/tensor/affine_grid.cc`)**:
- Checks `size_shape.NumDimensions() == 1` before indexing
`size_shape.GetDims()[0]` and reading `size_data[0..3]` /
`size_data[0..4]`. Without this check, a rank-0 `size` tensor aborts on
an empty `GetDims()` span, and enforcing rank 1 ensures
`size_shape.GetDims()[0]` equals the element count of `size_data`.

## Tests

- Added regression unit tests pinned to `DefaultCpuExecutionProvider()`
with `test.AddShapeToTensorData(false)` so dynamic runtime shapes reach
the CPU kernels:
- `ConvTest.Rank1InputAndWeightRejected` and
`ConvTest.Rank2InputAndWeightRejected` (`conv_op_test.cc`)
- `ConvIntegerTest.Rank1InputRejected` and
`ConvIntegerTest.Rank2InputAndWeightRejected` (`conv_integer_test.cc`)
  - `QLinearConvTest.Rank0InputRejected` (`qlinearconv_op_test.cc`)
- `CropAndResizeTest.InvalidInputRanksRejected`
(`crop_and_resize_op_test.cc`)
  - `Einsum.SubscriptLabelsExceedInputRankRejected` (`einsum_test.cc`)
- `AffineGridTest.size_input_is_rank_0` and
`AffineGridTest.size_input_rank_2_trailing_zero_rejected`
(`affine_grid_test.cc`)
- Verified in `onnxruntime_test_all`
(`--gtest_filter="ConvTest.*:ConvIntegerTest.*:QLinearConvTest.*:CropAndResizeTest.*:Einsum.*:AffineGridTest.*"`):
all 9 new regression tests fail or abort before the fix and pass (`9/9`)
with the fix applied, and the full 302-test filter passes with zero
regressions (`299 PASSED`, `3 SKIPPED`).

---
*Note: This patch was prepared with AI assistance and verified by human
review and local test execution.*


)

### Description
<!-- Describe your changes. -->

Simplify the shutdown-order fix proposed in microsoft#33267 by @akasakariko. This
PR branches off of microsoft#33267.

The shutdown-order fix is one synchronous internal diagnostic dispatch,
plus its lifetime-invariant comment. Remove the additional `atexit`
shutdown callback, static `Shutdown()` conversion, and final-shutdown
suppression latch. Existing teardown remains responsible for flushing
and joining SDK workers. Clarify that a zero teardown-upload budget does
not bound cancellation or worker draining. A small downstream SDK patch
also replaces its deliberately non-destructed factory's heap allocation
with non-destructed static storage, preserving shutdown safety without
leaking on shared-library unload.

Add dedicated, isolated desktop CTests instead of enabling telemetry
throughout ordinary CI tests:

- Four mutex-lifetime cases use the real `Env::Default()` singleton and
SDK PAL worker, initializing on the main thread or an application
thread, with enabled and disabled controls. Test-only observers require
callback completion, native worker join, and worker release before
debug-mutex retirement. Any unexpected upload fails through a no-network
HTTP module.
- Seven transport cases use the real SDK HTTP factory and
WinHTTP/curl/Apple transport against a parent-owned `127.0.0.1`
collector: upload, application-thread initialization, retry after HTTP
503, teardown with a pending response, environment opt-out, unit-test
suppression, and CI suppression. Windows/Linux additionally exercise
controlled DLL/shared-library reload.
- Payload assertions require distinct synthetic events before disabling
and after re-enabling, and reject the event logged while disabled.
Native terminal callbacks must complete exactly once; pending requests
must be cancelled and drained.
- A runner regression test rejects hostname lookup while binding the
numeric loopback collector.

Configuration/observation hooks exist only in generated test copies of
the provider. The forwarding HTTP module forces every request, including
retries, to the loopback collector. Test-only WinHTTP uses direct access
rather than automatic proxy discovery; curl proxy variables are
cleared/bypassed. SDK network detection is disabled. Each child has
private cache storage, and Windows HKCU/device-ID access is isolated
under a child-specific test key. Production configuration, public APIs,
and CI suppression are unchanged.

The reload case explicitly destroys its provider and exits its calling
thread before unloading, allowing thread-local destructors to finish,
then repeats after reload. Its isolated host also cleans up its private
curl global state after all users drain; production SDK code cannot
assume it owns other curl users. It does not claim that `FreeLibrary`
alone tears down an active SDK: testing showed that an active MSVC
worker can retain the DLL. Executable cases separately exercise normal
singleton destruction at process exit.

Rename the mutex executable to
`onnxruntime_telemetry_mutex_lifetime_test` to avoid colliding with
microsoft#33291's independently scoped shutdown target. The existing mutex CTest
names remain unchanged. See
`onnxruntime/test/platform/telemetry_1ds/README.md` for the coverage
matrix, commands, and limits.

### Motivation and Context
<!-- - Why is this change required? What problem does it solve?
- If it fixes an open issue, please link to the issue here. -->

Addresses microsoft#33251. Credit to @akasakariko for microsoft#33267's diagnosis, macOS
reproduction work, and synchronous SDK mutex initialization approach.

Production telemetry belongs to the function-local
`PosixEnv`/`WindowsEnv` returned by `Env::Default()`, not to the public
`OrtEnv` handle. Initializing the SDK mutex during that singleton's
constructor establishes the required reverse destruction order: the
existing Env destructor stops and joins the SDK workers before the mutex
is destroyed. This holds whether initialization occurs on the main
thread or an application thread.

The simpler fix relies on that ownership invariant. It does not promise
arbitrary heap-retained provider lifetimes or construction after static
teardown begins. The new transport coverage closes the ordinary CI
suppression gap without sending events to an external collector.

microsoft#33291 remains separate and necessary: Windows DLL process termination
can leave locks owned by terminated threads, requiring an early guard
before acquiring ORT/SDK locks. This PR neither incorporates that
production fix nor substitutes for its `ExitProcess`/DLL-process-detach
regression.

**Validation:** targeted archive-backed builds compile the changed
provider and test sources against cached ORT common and the pinned SDK
**v3.10.279.1**. These are not fresh full ORT builds.

| Platform | Results |
| --- | --- |
| Windows, Visual Studio 2026, RelWithDebInfo | All 12 CTests passed,
including 10 consecutive repetitions per case; no skips. |
| WSL/Linux, GCC 13, RelWithDebInfo | All 12 CTests passed, including 10
consecutive repetitions per case; no skips. Linux reload additionally
asserts that `dlclose` actually unloads the fixture. |

On each platform, negative controls remove the eager dispatch from the
generated provider: all 20 enabled/main-thread and application-thread
runs detected the ordering defect with the specific exit code 21; all 20
disabled controls passed. Forcing suppression into either enabled
initialization mode correctly failed with exit code 32.

Repository `lintrunner` and `git diff --check` passed. Native macOS,
TLS/certificate policy, and a fresh full ORT build have not been run
locally; local HTTP transport tests do not establish those results.

**CI integration follow-up:** the failed jobs on `3e41e9dace` exposed
two build issues in the fixtures: the mutex target did not inherit the
common library's private generated tenant-header include directory, and
MSVC rejected `std::getenv` as deprecated. The mutex target now inherits
those private includes, matching the transport targets; the transport
test uses the existing bounded, platform-safe telemetry environment
reader without adding a warning suppression.

The local validation harness now keeps the generated-header include
private, matching the real build, and Windows fixture compilation
enforces `/WX /we4996`. With these stricter settings, the rebuilt
fixtures passed all 12 CTests on Windows and all 12 on WSL/Linux, with
no skips.

**Native CI follow-up:** the jobs on `1fd9eb3b84` exposed macOS
transport timeouts and Linux LeakSanitizer failures in the reload case.
Even suppressed macOS cases spent about 35 seconds before completion;
Python's default `HTTPServer.server_bind` performs an unnecessary
reverse-DNS lookup. The collector now binds numerically without DNS,
with a regression that fails against the original bind implementation.
Native macOS confirmation remains pending.

Linux reload leak detection found the SDK's deliberately leaked
`LogManagerFactory` heap singleton and private static curl global
allocations. The SDK patch uses the same non-destructed static-storage
pattern as its PAL, rather than reintroducing unsafe static destruction.
The reload fixture explicitly releases curl globals only after its owned
provider has drained. No sanitizer suppressions, skipped tests, or
larger timeouts were introduced.

Latest targeted validation still uses cached common/SDK archives,
recompiling the patched SDK factory/provider objects from a pristine,
hash-verified v3.10.279.1 archive. Linux now links the cached private
static curl/mbedTLS closure, matching CI instead of system curl.

| Command | Result |
| --- | --- |
| `ctest --test-dir <windows-build> -C RelWithDebInfo -R
'^onnxruntime_telemetry_(shutdown\|transport)_' --output-on-failure` |
Passed all 13 CTests on Windows/VS2026; no skips. |
| `ctest -R onnxruntime_telemetry_ --output-on-failure` (WSL/Linux GCC
13 build with `-fsanitize=address`) | Passed all 13 CTests, including
actual unload/reload, with leak detection enabled; no skips.
Dependencies are cached archives, not fully sanitizer-rebuilt. |
| `lintrunner` | Passed. |
| `git diff --cached --check` | Passed. |

**Platform scope correction:** CI on `b2afb68424` confirms that all
seven native macOS subprocess transport modes and the shutdown cases
pass, as does the full Linux Debug ASan job. The remaining macOS failure
is the reload fixture: its Objective-C image stays resident after
`dlclose`, so the second load reuses static observations rather than
starting fresh; loading two SDK copies also registers duplicate
Objective-C classes. Limit this fixture to Windows/Linux instead of
adding Apple loader workarounds. No production code, assertions, or
timeouts change. Both local Windows and Linux ASan runs again passed all
13 CTests with no skips; an Apple-branch CMake registration check
confirmed all 12 supported tests remain registered (configuration only,
not native macOS execution).

The separate Linux WebGPU job failed while configuring Dawn because its
fetched Vulkan-Headers source lacked `CMakeLists.txt`, before telemetry
tests ran. This change does not modify Dawn. Full CI for the latest
follow-up is pending.

---------

Co-authored-by: KayanoLiam <Kayano04@outlook.jp>
Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Co-authored-by: Copilot Autofix powered by AI <62310815+github-advanced-security[bot]@users.noreply.github.com>
Copilot-Session: 4f59721f-9794-4779-99d4-ff50e0491c7d
Copilot-Session: e48d5a61-4aae-4f56-812e-3e0ac76760f5
Copilot-Session: e8c5bcc2-49b2-43fb-be53-ffb2f6caeb70

…n experts average >= 24 rows (microsoft#33714)

### Description

`RunPackedGroupedGemm` in `moe_int2_prefill.cu` runs the CUTLASS INT4
grouped GEMM of the QMoE INT2/INT3 prefill path: raw INT2/INT3 weights
are repacked to the SM80 INT4 layout first, then FC1 and FC2 go through
this GEMM. It hard-coded the 32-row tile
`CtaShape32x128x64_WarpShape32x32x64`. That tile is too small once the
experts average about 24 or more rows; Qwen3.8-Flash-Next (hidden 2560,
intermediate 640, 512 experts, top-10, block size 64) has 40 rows per
expert at a 2048-token prefill chunk.

This PR picks the tile from `rows_per_expert = expanded_rows /
num_experts`: `CtaShape64x128x64_WarpShape64x32x64` for 24 or more,
`CtaShape32x128x64_WarpShape32x32x64` below. It is the crossover that
`PickPrefillTactic` in `moe_quantization.cc` already uses for the INT4
layers. Chunks with fewer than 24 rows per expert (1024 tokens and less
in the model above) keep the 32-row tile, so nothing changes for them.

Only the CTA and warp tiling changes. The K loop (64-wide tiles, the
group-wise dequantization, the `m16n8k16` MMA) and the epilogue are the
same, so every output element accumulates in the same order.

#### Summary of Changes

| File | Change |
|------|--------|
| `onnxruntime/contrib_ops/cuda/llm/moe_gemm/moe_int2_prefill.cu` |
`RunPackedGroupedGemm` (the `weight_bits == 4` CUTLASS branch) selects
the CTA/warp tile from the average rows per expert instead of always
using 32x128x64. |
| `onnxruntime/test/contrib_ops/moe_test.cc` |
`QMoETest_Int3AndMixedWidthCudaPrefillParity` gets three 64-row cases,
`{3, 3, 64, 64, 0}`, `{3, 4, 32, 64, 0}` and `{4, 3, 128, 64, 0}`. 64
rows with top_k 2 over 4 experts are 32 rows per expert, so the 64-row
tile runs. The existing cases (at most 19 rows over 4 experts) stay on
the 32-row tile. |

### Motivation and Context

Measured on H200 (SM90, batch 1) with the two mixed INT4/INT3
Qwen3.8-Flash-Next packages, against a build that selects the 64-row
tile at 24 or more rows per expert (an earlier version of this path
did):

- `nsys` of a 2048-token prefill chunk, layer 14: the INT4 grouped GEMMs
take 899 us (FC1) and 533 us (FC2) on the 64x128x64 tile and 966 us and
584 us on 32x128x64, i.e. 7.5% and 9.6% longer. Over the last prefill
step the MoE GEMM time is 67.88 ms against 73.04 ms (+5.16 ms), which is
about 89% of the 5.8 ms TTFT difference at 2048 tokens.
- With the 32-row tile, TTFT at 2048, 8192 and 32768 prompt tokens is
2.2-3.2% above that build. With this change the difference is -0.1% to
+0.3%.
- The generated token sequences of the packages are identical with and
without the change (144 decode runs).

### Testing

Validated on H200 with an in-tree CUDA EP build
(`onnxruntime_ENABLE_CUDA_EP_INTERNAL_TESTS=ON`, SM90), on this commit
together with the tips of microsoft#33689 and microsoft#33707. The change does not depend
on them: trial merges of this branch with microsoft#33689, microsoft#33707, microsoft#33650 and
microsoft#32126 are conflict-free in any order (microsoft#33689 also edits `moe_test.cc`,
in other hunks).

- `MoETest.QMoETest_Int3AndMixedWidthCudaPrefillParity` (FP16 and BF16,
13 cases each) passes. `nsys` of this test shows the new rows reach the
new tile: per data type, 22 launches of
`MoeFCGemm<DqMmaMultistage<GemmShape<32, 128, 64>>>` and 6 of
`GemmShape<64, 128, 64>` (3 cases, FC1 and FC2). Before this change the
test cannot launch the 64-row kernel.
-
`MoETest.QMoETest_Int3*:MoETest.QMoETest_Int2Cuda*:MoETest.QMoETest_MixedWidthCuda*:*QMoECudaInt3*`:
45 run, 45 passed.
- `MoETest.*:*QMoE*`: 131 run, 118 passed, 13 skipped (the CPU QMoE
cases and the two Mixtral cases, which these CUDA builds skip, and the
routing-statistics test for the plugin EP), 0 failed.
- `lintrunner` on the two files: no issues.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>


ai-fw-intg
requested review from
Jaswanth51,
ankitm3k,
jatinwadhwa921 and
vthaniel
October 29, 2026 20:39

hdharpure9922
self-requested a review
October 30, 2026 04:34


This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment



Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Automated daily backmerge from ORT main to ovep-develop. No conflicts detected. Do NOT squash or rebase - use merge commit only.